Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
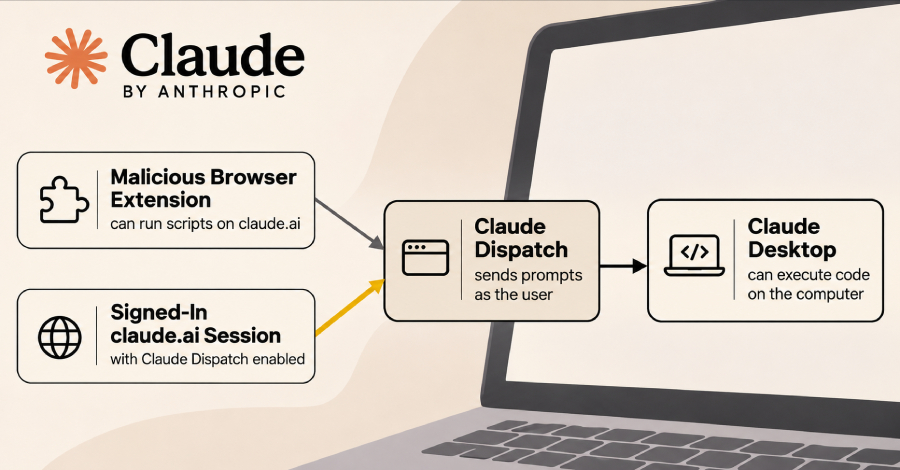
Malicious Browser Extensions Could Use Claude Dispatch to Run Code on Users‘ Computers
A browser extension that can run scripts on claude.ai could make Claude Desktop run code on a person's computer, researchers...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-92396: Medium Schwachstelle
The ShopEngine Gutenberg WooCommerce Builder Blocks Addon WordPress plugin before 2.4.4 does not validate the user's capabilities or the ownership...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-39744: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in WC Lovers WCFM Membership wc-multivendor-membership allows Stored XSS.This...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-119488: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Shamim Rajani Pie Register pie-register allows Stored XSS.This...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-87964: High Schwachstelle
The Product Feed Manager for WooCommerce – CTX Feed – Support 220+ Shopping, AI & Social Channels plugin for WordPress...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-110776: High Schwachstelle
The MDTF – Meta Data and Taxonomies Filter plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the 'vars'...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-110291: High Schwachstelle
The Graphina – Charts and Graphs For Elementor plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the 'iq_tree_chart_node_font_family...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-116592: High Schwachstelle
undici is an HTTP client for Node.js. In versions 7.30.1 and 8.12.2 through 8.12.3, when an originless Agent composes the...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-19877: High Schwachstelle
INFINITT ULite 5.0.2.1_BN48_20260528 and earlier protects image-share links with a low-entropy password and does not restrict repeated password attempts, allowing...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-86606: High Schwachstelle
The iubenda | All-in-one Compliance for GDPR / CCPA Cookie Consent + more WordPress plugin before 3.13.7 does not properly...