Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-115673: High Schwachstelle
The Anti-Spam, Spam FireWall by CleanTalk WordPress plugin before 6.91 does not escape a commenter-supplied value before outputting it on...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-88801: High Schwachstelle
The MDJM Event Management and Mobile Events Manager WordPress plugins through 1.7.8.7 do not check a capability or a nonce...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-110532: High Schwachstelle
The Mail Mage WordPress plugin through 0.0.25 does not properly sanitise and escape a user-supplied value before using it in...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-119516: Critical Schwachstelle
Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking allows Object...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-113615: Critical Schwachstelle
The GS JWT Authentication for WP REST API WordPress plugin through 1.0.0 does not sanitize or parameterize a request value...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-118423: Critical Schwachstelle
The WP Libre Form WordPress plugin 1.5.0.1 does not validate the type of files uploaded through its form submissions, allowing...
 ANWENDUNGSSICHERHEIT
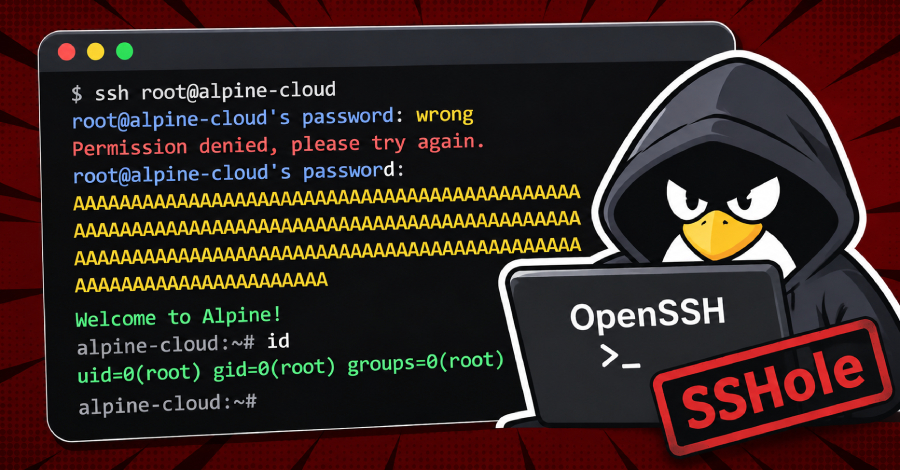
Hackers Target OpenSSH SSHole Flaw Within Hours of Disclosure, Gain Root on Honeypot
Threat actors are attempting to exploit a recently disclosed security flaw impacting OpenSSH that can enable sign-ins to accounts that...
 ANWENDUNGSSICHERHEIT
Installing the Fix for an Exploited WordPress Flaw Can Expose Some Sites One Last Time
Some WordPress sites can still be attacked while they install the fix for an actively exploited flaw, according to Umut...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-91049: Medium Schwachstelle
The EWWW Image Optimizer WordPress plugin before 8.9.1 does not properly sanitize and restrict a value in post content before...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-107773: Medium Schwachstelle
The Dokan: AI Powered WooCommerce Multivendor Marketplace Solution WordPress plugin before 5.3.3 does not correctly verify authorization when serving a...