Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-100109: Critical Schwachstelle
The Security For WooCommerce WordPress plugin from 1.0.10 to 1.0.16 does not perform capability checks when creating users through an...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-19256: Critical Schwachstelle
The All In One Login WordPress plugin before 2.5.0 does not adequately restrict the number of attempts that can be...
 ANWENDUNGSSICHERHEIT
ThreatsDay: Apache OFBiz RCE, DreamHost Breach, DeFi Site Hijacks + 17 More Stories
How much damage can someone do without breaking much? Quite a lot, it seems. A stolen login can open doors...
 ANWENDUNGSSICHERHEIT
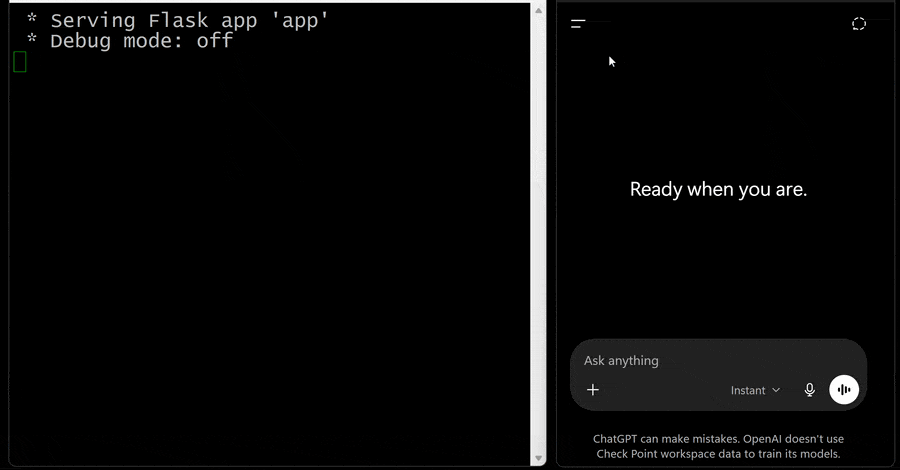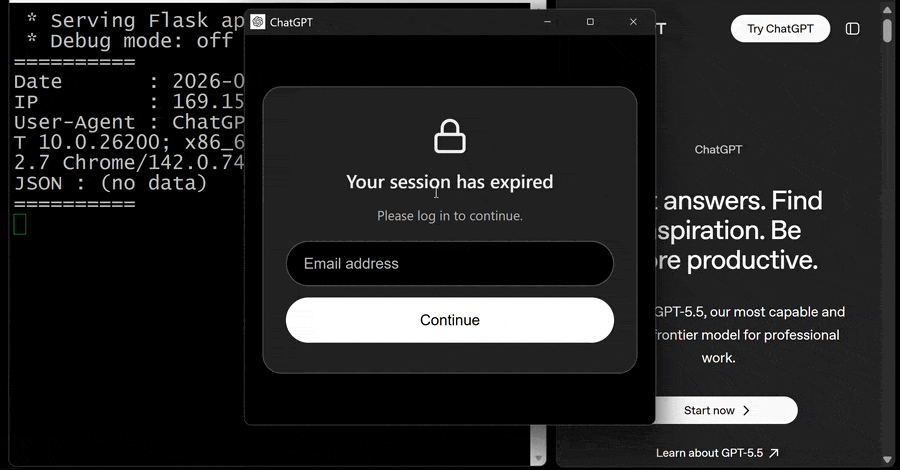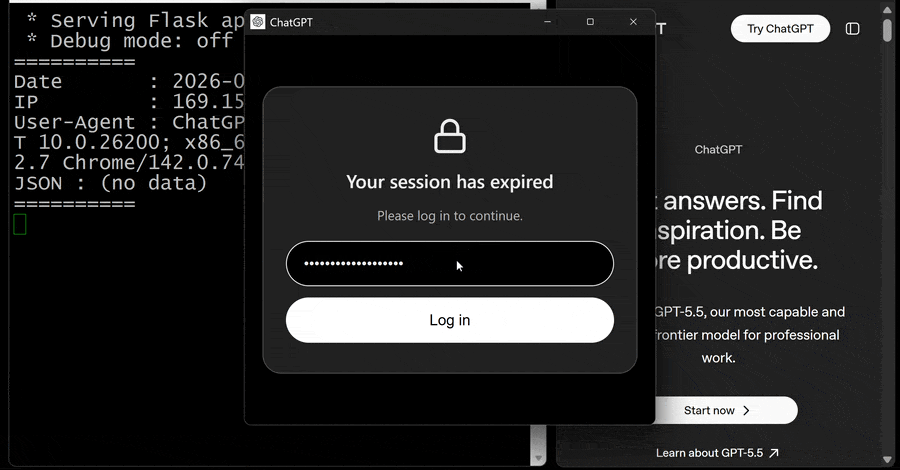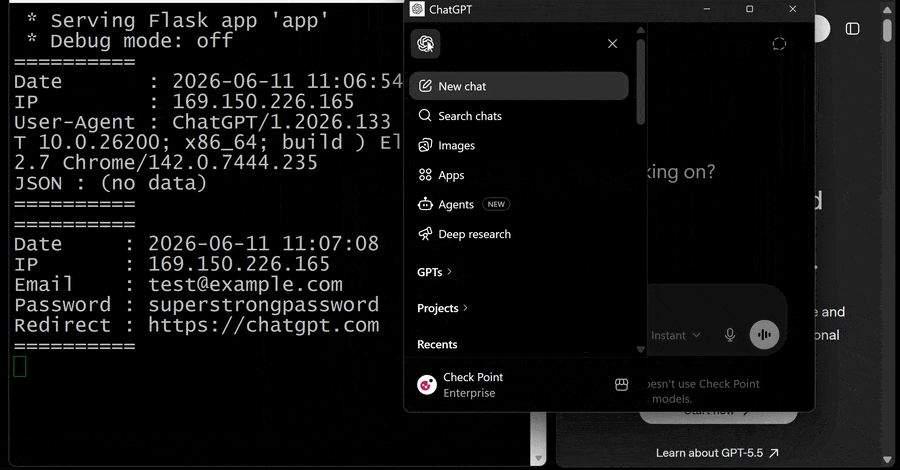
Researchers Bypass ChatGPT Lockdown Mode to Exfiltrate Chats Without User Interaction
Cybersecurity researchers have disclosed details of a now-patched vulnerability that could be exploited to bypass Lockdown Mode protections in OpenAI...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-62007: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Unlimited Elements Unlimited Elements For Elementor (Free Widgets,...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-57666: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Aguila Technologies WP Customer Area customer-area allows Reflected...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-57639: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Roland Murg WP Booking System wp-booking-system allows Reflected...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-54861: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Aguila Technologies WP Customer Area customer-area allows Reflected...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-119477: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Jacob N. Breetvelt WP Photo Album Plus wp-photo-album-plus...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-119366: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in AdvancedCoding wpDiscuz wpdiscuz allows Stored XSS.This issue affects...