Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-79697: Critical Schwachstelle
A vulnerability was determined in Advantech WISE-6610-NB, WISE-6610-EB, WISE-6610-TB, WISE-6610-JB, WISE-6610-CB, WISE-6610-EL-NB, WISE-6610-EL-EB, WISE-6610-EL-TB, WISE-6610-EL-JB, WISE-6610-EL-CB, W...
 ANWENDUNGSSICHERHEIT
Telerik UI Padding-Oracle Bug Chained to Unauthenticated RCE — Public Exploit Released
A TantoSec proof-of-concept turns an AES-CBC "padding oracle" in Telerik UI for ASP.NET AJAX into unauthenticated remote code execution —...
 ANWENDUNGSSICHERHEIT
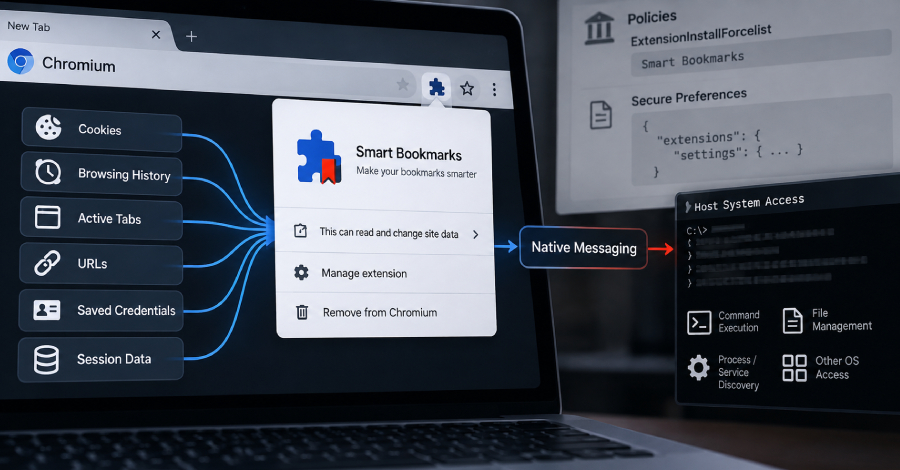
PEEP Turns Chrome and Edge Into Post-Compromise Backdoors for Host Command Execution
Cybersecurity researchers have disclosed details of a complex Chromium-based post-exploitation toolkit called PEEP that masquerades as a bookmarks extension for...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-86171: Medium Schwachstelle
A security vulnerability has been detected in DefaultFuction CRM 1.0.0. This affects an unknown function of the file /modules/orders/delete.php. Such...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-86170: Medium Schwachstelle
A weakness has been identified in DefaultFuction CRM 1.0.0. The impacted element is an unknown function of the file /modules/orders/edit.php....
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-83534: Medium Schwachstelle
PostgreSQL Anonymizer contains a vulnerability in the anon.anonymize_database_parallel() function that allows the owner of a table to run arbitrary code...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-19634: Medium Schwachstelle
PostgreSQL Anonymizer contains a SQL injection vulnerability in two import functions. A user can create a malicious JSON document containing...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-84028: Medium Schwachstelle
The Bold Page Builder WordPress plugin before 5.9.9 does not sanitise and escape a shortcode attribute before outputting it in...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-86225: High Schwachstelle
A vulnerability was identified in SourceCodester Class and Exam Timetabling System 1.0. Affected by this vulnerability is the function mysqli_query...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-86224: High Schwachstelle
A vulnerability was determined in SourceCodester Class and Exam Timetabling System 1.0. Affected is the function mysqli_query of the file...