Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
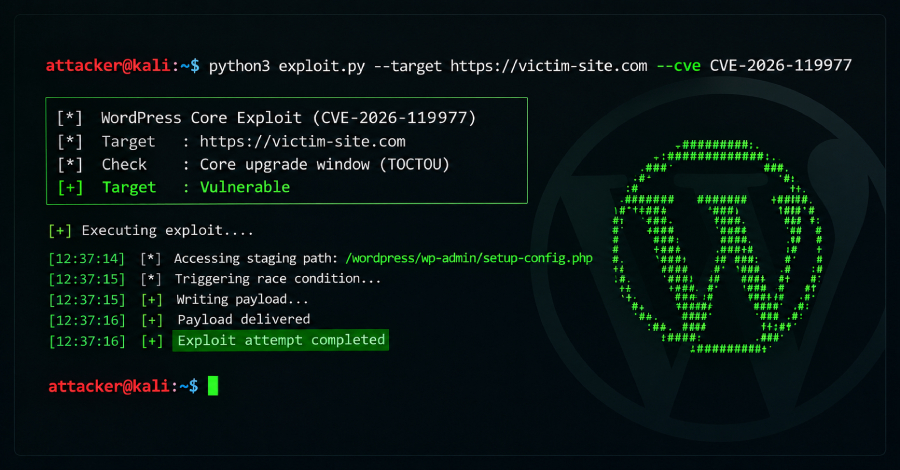
CISA Confirms Hackers Exploiting WordPress Core Flaw During Software Upgrades
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a security flaw in WordPress Core to the Known Exploited...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-118871: Medium Schwachstelle
SQL injection vulnerability classified as an internal threat level.Attackers can steal database information via SQL injection while logged in.
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-91907: Medium Luecke in Dell Openmanage_Enterprise
Dell OpenManage Enterprise, versions prior to 4.8.0, contains an Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability....
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-120318: High Schwachstelle
Product Gallery Slider & Additional Variation Images for WooCommerce 2.3.23 before 2.3.26 contains a missing authorization vulnerability in Codestar backup...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-120349: High Schwachstelle
A security flaw has been discovered in dayrui XunRuiCMS up to 4.7.4. Affected by this issue is the function str_replace...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-120348: High Schwachstelle
A vulnerability was identified in dayrui XunRuiCMS up to 4.7.4. Affected by this vulnerability is the function _get_tpl_content of the...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-120347: High Schwachstelle
A vulnerability was determined in dayrui XunRuiCMS up to 4.7.4. Affected is the function View of the file dayrui/Fcms/Core/View.php of...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-120426: High Schwachstelle
OpenCSG CSGHub through v2.6.0-ce contains an authorization bypass vulnerability in the unauthenticated file resolve route that allows remote attackers to...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-74993: High Schwachstelle
Improper neutralization of special elements used in an SQL command ('SQL injection') vulnerability in Starnet Computer and Network Systems Inventory...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-94349: High Luecke in Dell Openmanage_Enterprise
Dell OpenManage Enterprise, versions prior to 4.8.0, contains an Improper Neutralization of Special Elements used in an OS Command ('OS...