Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
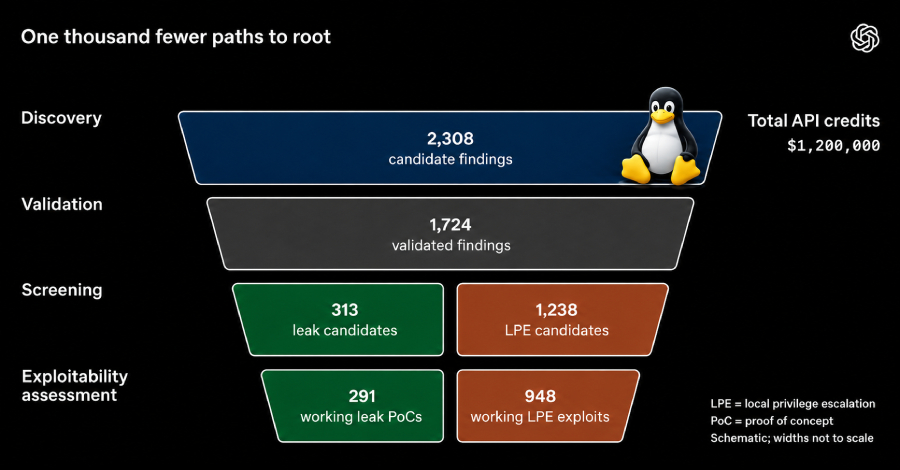
OpenAI AI Pipeline Generates 948 Linux Root Escalation Exploits in 30-Hour Run
OpenAI on Wednesday detailed a pipeline that employed an upcoming cyber-focused artificial intelligence (AI) model to validate and patch 948...
 ANWENDUNGSSICHERHEIT
Hackers Exploit Patched Apple Flaw to Deliver Info-Stealing Malware, CISA Says
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a medium-severity security flaw impacting multiple Apple operating systems...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-91075: Medium Schwachstelle
The Eupago Gateway For Woocommerce WordPress plugin from 4.5.0 through 4.7.5 does not verify the authenticity of incoming payment-confirmation webhook...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-103327: Medium Schwachstelle
The CryptoCloud WordPress plugin from 3.0.0 through 3.0.1 does not verify the authenticity of the payment notifications received by its...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-103379: Medium Schwachstelle
The WATI Chat and Notification WordPress plugin through 1.1.8 does not require a valid, non-empty secret on a public endpoint...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2025-5769: Medium Schwachstelle
The authentication endpoint does not properly encode user-supplied input before rendering it within the web page. This lack of output...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-121458: Medium Schwachstelle
Instatic before 0.0.21 contains a missing authorization vulnerability in its AI/MCP content read tools that allows low-privileged authenticated users with...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-119843: Medium Schwachstelle
A flaw was found in GStreamer's gst-plugins-good package. The FLV media demuxer does not properly validate buffer sizes and data...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-121022: High Schwachstelle
Use of Default Password (CWE-1393) in the web client in AxxonSoft Axxon One before 3.0.0 on Windows and Linux allows...
 ANWENDUNGSSICHERHEIT
Barracuda Flaws Could Be Chained to Bypass Authorization and Gain Root Access
Barracuda has disclosed details of two vulnerabilities affecting its products that, if chained together, could allow an attacker to bypass...