Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-45558: Critical Schwachstelle
Roxy-WI is a web interface for managing Haproxy, Nginx, Apache and Keepalived servers. In versions 8.2.6.4 and prior, the HAProxy...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-45556: Critical Schwachstelle
Roxy-WI is a web interface for managing Haproxy, Nginx, Apache and Keepalived servers. In versions 8.2.6.4 and prior, POST /waf///rule//save...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-45552: Critical Schwachstelle
Roxy-WI is a web interface for managing Haproxy, Nginx, Apache and Keepalived servers. In versions 8.2.6.4 and prior, the install...
 ANWENDUNGSSICHERHEIT
Unpatched Langflow Flaw CVE-2026-5027 Exploited for Unauthenticated RCE
A high-severity unpatched security flaw in Langflow, an open-source low-code platform to build artificial intelligence (AI) applications, has come under...
 ANWENDUNGSSICHERHEIT
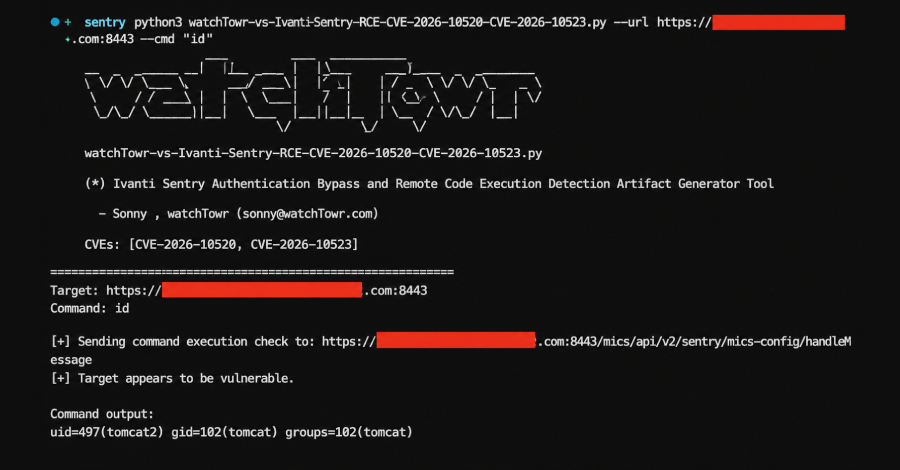
Ivanti, Fortinet, and SAP Release Patches for Multiple Critical Vulnerabilities
Fortinet, Ivanti, and SAP have released security updates to address multiple critical security vulnerabilities that could result in arbitrary code...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2025-40808: Medium Schwachstelle
A vulnerability has been identified in SIPROTEC 5 6MD84 (CP300) (All versions), SIPROTEC 5 6MD85 (CP200) (All versions), SIPROTEC 5...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-25688: Medium Luecke in Apache Answer
Improper Neutralization of Alternate XSS Syntax vulnerability in Apache Answer. This issue affects Apache Answer: through 2.0.0. AI-generated response content...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-8677: Medium Schwachstelle
The Prime Elementor Addons – Lightweight Elementor Widgets for Faster Pages plugin for WordPress is vulnerable to Stored Cross-Site Scripting...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-8599: Medium Schwachstelle
The MailerPress – Email Marketing, Newsletter, Email Automation & WooCommerce Emails plugin for WordPress is vulnerable to Stored Cross-Site Scripting...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-7542: Medium Schwachstelle
The Slider Revolution plugin for WordPress is vulnerable to Sensitive Information Disclosure in versions up to and including 7.0.10. This...