Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
Claude Opus 4.6 Bypasses Gym Booking Limit, Cancels Other Users‘ Reservations in Tests
Aikido Security has published research that recreates the Australian gym-booking incident in a synthetic environment, finding that Claude Opus 4.6,...
 ANWENDUNGSSICHERHEIT
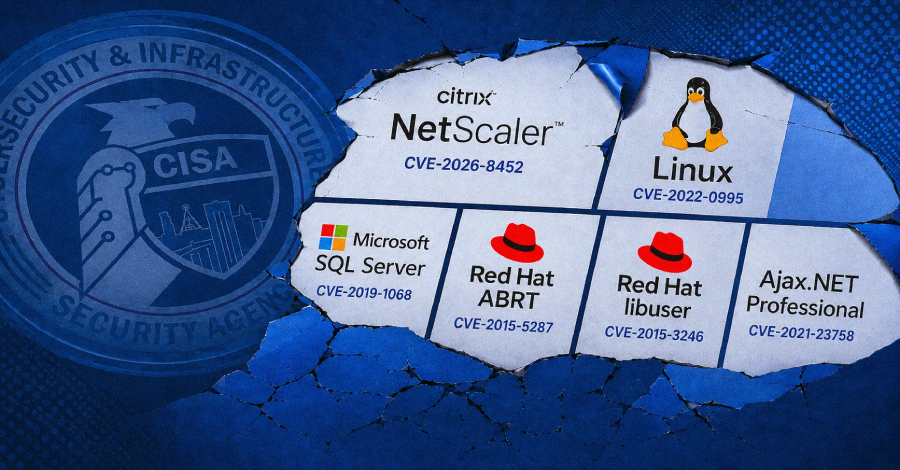
CISA Adds Six Exploited Flaws to KEV, Including NetScaler, Linux, and SQL Server Bugs
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added six flaws to its Known Exploited Vulnerabilities (KEV) catalog,...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-78470: Medium Schwachstelle
The WP Project Manager Pro plugin for WordPress is vulnerable to SQL Injection in all versions up to, and including,...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-75971: High Schwachstelle
The ShopEngine Elementor WooCommerce Builder Addon – All in One WooCommerce Solution plugin for WordPress is vulnerable to Privilege Escalation...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78563: High Schwachstelle
The NotificationX Pro plugin for WordPress is vulnerable to Stored Cross-Site Scripting in all versions up to, and including, 3.1.4...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-18328: High Schwachstelle
The Forminator Forms – Contact Form, Payment Form & Custom Form Builder plugin for WordPress is vulnerable to DOM-Based Reflected...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-18323: High Schwachstelle
The Forminator Forms – Contact Form, Payment Form & Custom Form Builder plugin for WordPress is vulnerable to Stored Cross-Site...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78576: High Schwachstelle
The Readabler plugin for WordPress is vulnerable to SQL Injection in all versions up to 2.0.18 (exclusive) due to insufficient...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-79667: High Schwachstelle
Ech0 version 4.3.4 and earlier fails to reliably enforce scoped access token (least-privilege) restrictions on several privileged admin routes. Multiple...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78572: High Schwachstelle
The Kalles Addons plugin for WordPress is vulnerable to PHP Object Injection in all versions up to, and including, 1.0.6...