Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-16231: High Schwachstelle
hbs is an Express view engine that wraps Handlebars. Its registerAsyncHelper API bypasses Handlebars' automatic HTML escaping: an async helper...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-59335: High Schwachstelle
Improper handling of case sensitivity (CWE-178) in the identity zone authorization check in the Identity Zone Endpoint in Cloud Foundry...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-79665: High Schwachstelle
Ech0 before 4.5.1 contains an authorization bypass vulnerability where session tokens skip scope validation in RequireScopes middleware, allowing logged-in non-admin...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-19949: High Schwachstelle
The All-in-One WP Migration and Backup plugin for WordPress is vulnerable to SQL Injection via archive restore functionality in all...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-49845: Critical Schwachstelle
SQL injection in Hive Metastore direct SQL partition-name resolution in Apache Hive before 4.2.1 on all platforms allows authenticated users...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-78568: Critical Schwachstelle
The Total Donations plugin for WordPress is vulnerable to SQL Injection in all versions up to, and including, 2.0.5 due...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-63586: Critical Schwachstelle
The web-based management interface uses a modified uhttpd server with CGI shell scripts. The HTTP Basic Authentication username, taken directly...
 ANWENDUNGSSICHERHEIT
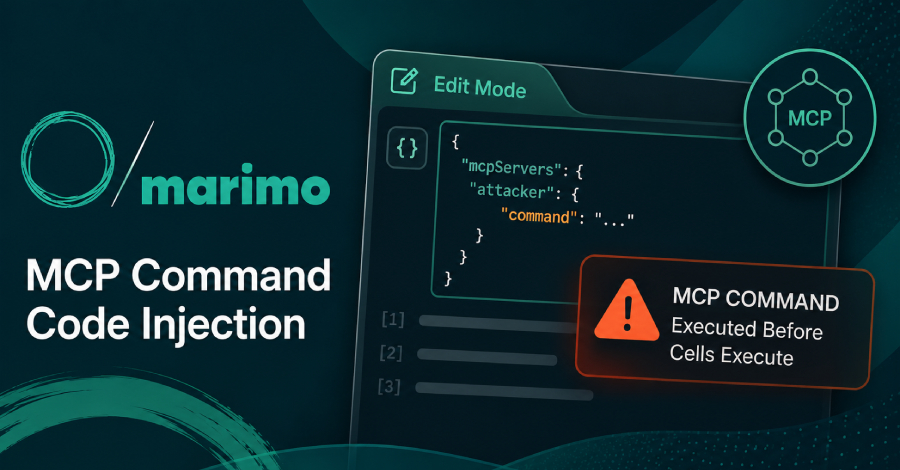
Marimo Notebook Flaw Could Run MCP Commands Before Cells Execute in Edit Mode
Marimo has addressed a high-severity security flaw in its notebook software that allowed an attacker to execute an attacker-supplied Model...
 ANWENDUNGSSICHERHEIT
Critical Gitea RCE Actively Exploited as Reported Attack Drops Miner-Like Payload
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday warned of active exploitation efforts targeting a recently patched critical...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78248: High Schwachstelle
A vulnerability was determined in SourceCodester Simple Online Food Ordering System 1.0. Impacted is an unknown function of the file...