Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-14829: High Schwachstelle
The Checkimate — WooCommerce Checkout, Abandoned Cart Recovery & Order Bumps WordPress plugin through 1.0.13 does not properly restrict access...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-55978: High Schwachstelle
An improper access control vulnerability in CatchPulse could allow a non-administrative local attacker to connect to an unrestricted kernel filter communication port and...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-16054: Critical Schwachstelle
The Drag and Drop Multiple File Upload for WooCommerce WordPress plugin before 1.1.8 does not prevent unauthenticated users from obtaining...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-12713: Critical Schwachstelle
The WPCargo Track & Trace WordPress plugin before 8.0.4 does not properly sanitise and escape a parameter before using it...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2025-15039: Critical Schwachstelle
The Conditional Authentication (Adaptive Authentication) script does not correctly enforce the completion of all required authentication steps when a specific...
 ANWENDUNGSSICHERHEIT
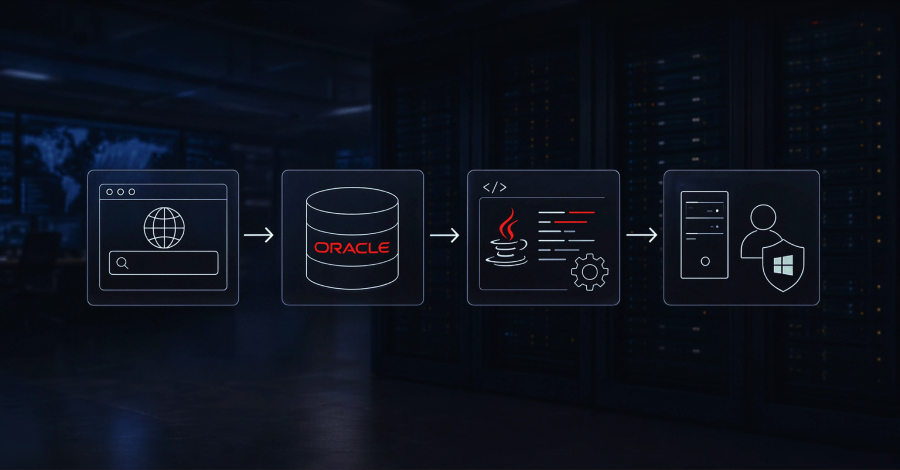
Attackers Compile khunt Inside Oracle to Turn SQL Injection Into Windows SYSTEM Access
Attackers broke into an organization's Oracle database through a SQL injection flaw in a public-facing web application, then installed a...
 ANWENDUNGSSICHERHEIT
AI Recommendation Poisoning: How „Ask AI“ Buttons Silently Alter LLM Memory
A new class of prompt injection is spreading across commercial websites. It requires no malware, no stolen credentials, and no...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-67592: High Schwachstelle
It was not possible to govern the maximum number of transfer frames per incoming delivery, enabling an authenticated attacker to...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-16736: High Schwachstelle
The User Registration & Membership WordPress plugin before 5.2.6 does not enforce the site's registration-disabled setting when processing registration-form submissions,...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-16603: High Schwachstelle
The Passster WordPress plugin before 4.3.6 does not enforce its category-based content protection on the WordPress REST API, allowing unauthenticated...