Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-86158: High Schwachstelle
Missing authentication in the local .NET backend (Fiddler.WebUi) of Progress Software Fiddler Everywhere 8.0.2 allows a local unauthenticated attacker to...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100776: High Schwachstelle
Use-after-free in the JavaScript: WebAssembly component. This vulnerability was fixed in Firefox ESR 153.4, Thunderbird 157, Thunderbird 140.17, Thunderbird 153.4,...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100769: High Schwachstelle
Use-after-free in the JavaScript: WebAssembly component. This vulnerability was fixed in Firefox ESR 153.4, Thunderbird 157, Thunderbird 140.17, Thunderbird 153.4,...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100768: High Schwachstelle
Use-after-free in the Graphics: WebGPU component. This vulnerability was fixed in Thunderbird 157 and Firefox 157.
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100765: High Schwachstelle
Use-after-free in the JavaScript: WebAssembly component. This vulnerability was fixed in Firefox ESR 153.4, Thunderbird 157, Thunderbird 153.4, and Firefox...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100764: High Schwachstelle
Privilege escalation due to incorrect boundary conditions in the Graphics: WebGPU component. This vulnerability was fixed in Thunderbird 157 and...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100761: High Schwachstelle
Privilege escalation due to use-after-free in the Graphics: WebGPU component. This vulnerability was fixed in Thunderbird 157 and Firefox 157.
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-84154: Critical Schwachstelle
A Code Injection vulnerability affecting GEOVIA Geospatial Data Manager from Release 3DEXPERIENCE R2024x through Release 3DEXPERIENCE R2026x could allow an...
 ANWENDUNGSSICHERHEIT
Kiteworks Fixes Critical Flaw Found During Nine-Hour Precautionary Shutdown
Kiteworks on Monday said it worked with federal intelligence authorities over the weekend as it identified and addressed a critical...
 ANWENDUNGSSICHERHEIT
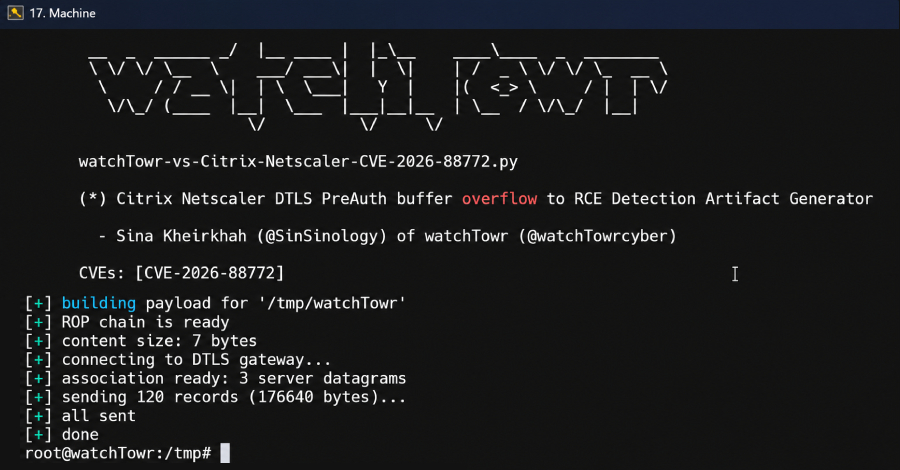
Citrix NetScaler CVE-2026-88772 Exploit Details Show Pre-Auth Path to Shellcode Execution
Cybersecurity researchers have disclosed technical details of a recently patched critical security flaw in Citrix NetScaler ADC and Gateway that...