Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-15241: High Schwachstelle
The AI ChatBot for WooCommerce WordPress plugin before 4.8.4 does not perform any authorization or nonce check on one of...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-68581: High Schwachstelle
Vikunja versions 0.22.0 through 2.3.0 fail to validate the principal type in API token management. Because user IDs and link-share...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-65321: Critical Schwachstelle
PyAthena prior to 3.35.4 contains a sql injection vulnerability that allows unauthenticated attackers to inject arbitrary SQL by exploiting improper...
 ANWENDUNGSSICHERHEIT
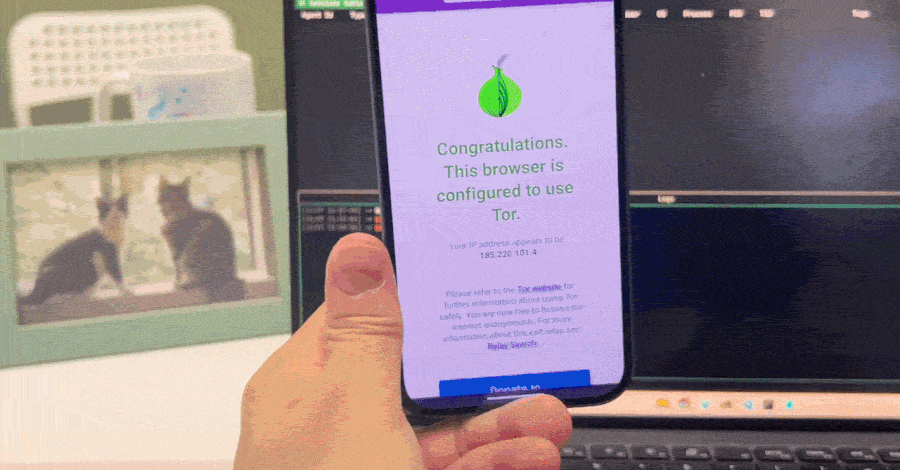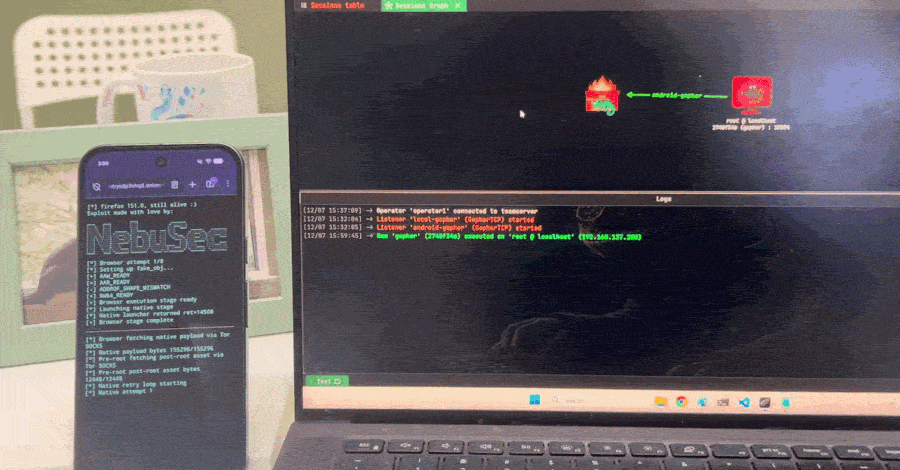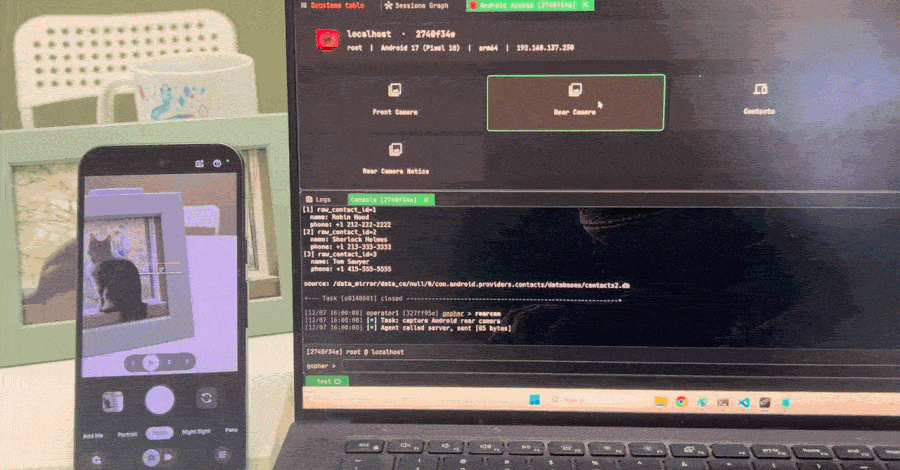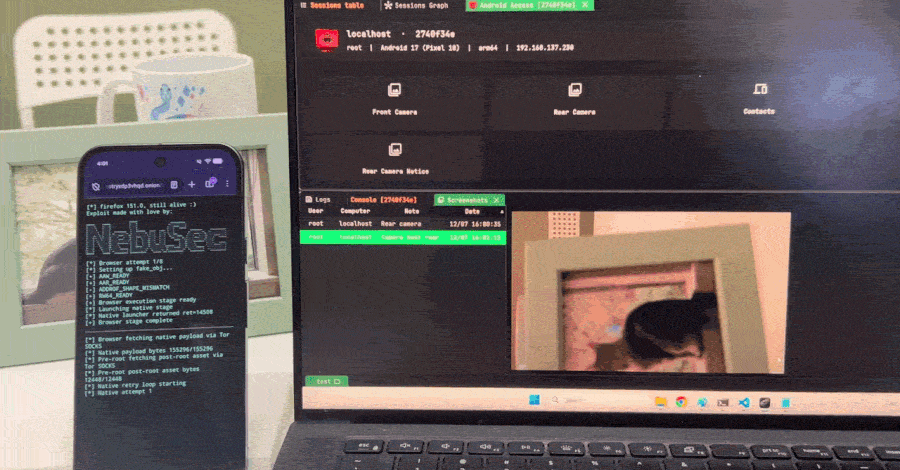
Researchers Show a Single Malicious Webpage Visit Can Compromise Tor Browser
Nebula Security says a patched Firefox JIT flaw could be triggered by simply visiting a malicious webpage and was also...
 ANWENDUNGSSICHERHEIT
N-able Says Attackers Take Over N-central Servers After Initial Fix Proves Incomplete
N-able said attackers exploited an authentication bypass in N-central to gain remote administrative access and reach the customer systems managed...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-18435: Medium Schwachstelle
The Kadence Blocks — Page Builder Toolkit for Gutenberg Editor plugin for WordPress is vulnerable to Stored Cross-Site Scripting via...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-18062: Medium Schwachstelle
The Kadence Blocks — Page Builder Toolkit for Gutenberg Editor plugin for WordPress is vulnerable to Stored Cross-Site Scripting via...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-16685: Medium Schwachstelle
The Download Manager plugin for WordPress is vulnerable to Stored Cross-Site Scripting via 'icon' Shortcode Attribute in all versions up...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-16684: Medium Schwachstelle
The Easy Property Listings plugin for WordPress is vulnerable to Stored Cross-Site Scripting via 'facebook' User Contact Method in all...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-16091: Medium Schwachstelle
The GamiPress – Gamification plugin to reward points, achievements, badges & ranks in WordPress plugin for WordPress is vulnerable to...