Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-69083: Critical Schwachstelle
SiYuan versions before v3.7.3 contain SQL injection vulnerabilities in the fullTextSearchAssetContent endpoint reachable by unauthenticated users and publish RoleReader tokens....
 ANWENDUNGSSICHERHEIT
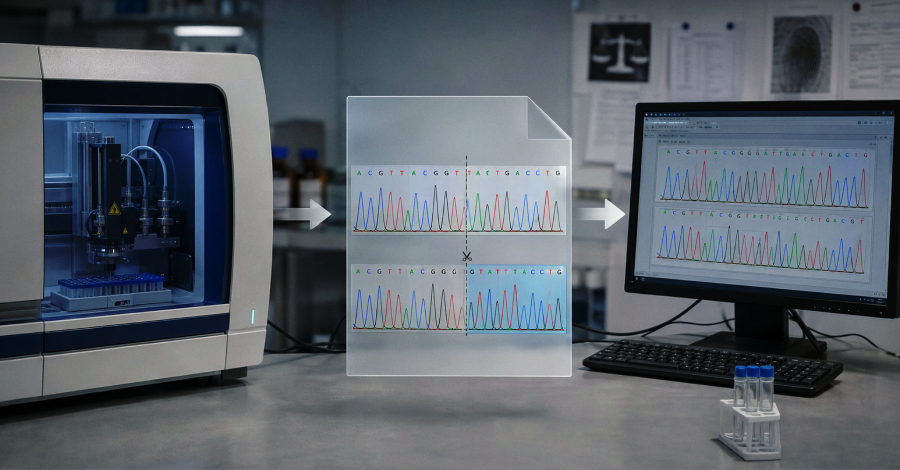
Thermo Fisher Patches Flaw That Could Make DNA File Tampering Nearly Undetectable
Thermo Fisher Scientific has patched a flaw in select Applied Biosystems human identification software that could allow data files to...
 ANWENDUNGSSICHERHEIT
CISA Adds Exploited N-able N-central Flaw to KEV After Customer Compromises
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a high-severity security flaw impacting N-able N-central to its...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-12231: Medium Schwachstelle
The Exclusive Addons for Elementor plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the ‘ exad_infobox_image’ parameter in...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-18573: Medium Schwachstelle
A flaw was found in the keycloak-services component of Keycloak, which is used for managing authentication and authorization flows. The...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-18572: Medium Schwachstelle
Keycloak provides authorization services that allow administrators to restrict access to resources based on time policies (for example, only allowing...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-13389: Medium Schwachstelle
The webtoffee-cookie-consent WordPress plugin before 3.5.3 does not perform authorization checks on several of its REST API routes, allowing unauthenticated...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-10848: High Schwachstelle
The OCPP 1.6 client in subsys/net/lib/ocpp parsed inbound WAMP RPC frames in parse_rpc_msg() (subsys/net/lib/ocpp/ocpp_j.c) using a hand-rolled helper, extract_string_field(), that...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-65875: High Schwachstelle
BaserCMS provided by baserCMS Users Community contains a CSV file injection vulnerability. If a user downloads and opens a CSV...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-16285: High Schwachstelle
The Product Attachment for WooCommerce WordPress plugin before 2.3.3 does not perform any authorization check before streaming media library files,...