Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-77874: High Schwachstelle
IBM Enterprise Build of Quarkus 3.27.1 through 3.27.5.SP1, and 3.33.1 through 3.33.3.SP1 is vulnerable to SQL injection. A remote unauthenticated...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78311: High Schwachstelle
SQL Injection vulnerability in DIAEnergie. This issue affects DIAEnergie: before 1.11.00.022.
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78309: High Schwachstelle
SQL Injection vulnerability in DIAEnergie. This issue affects DIAEnergie: before 1.11.00.022.
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-51994: Critical Schwachstelle
mcp-remote versions 0.1.32 through 0.1.38 are vulnerable to Server-Side Request Forgery (SSRF) via the resource_metadata URL extracted from a remote...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-12227: Critical Schwachstelle
The Visual Composer Website Builder plugin for WordPress is vulnerable to Local File Inclusion in all versions up to, and...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-97359: Critical Schwachstelle
HFS2 version 2.4.0 and earlier contains a template injection vulnerability in the multipart upload handler that allows unauthenticated attackers to...
 ANWENDUNGSSICHERHEIT
ThreatsDay: AI Search Poisoning, AI Coding Tool Leaking Repos, One-Click Code Execution and 13 More
This week, the dangerous stuff keeps arriving dressed as something boring. An update. A login box. A search answer. A...
 ANWENDUNGSSICHERHEIT
WSO2 and Adobe Commerce Flaws Exploited in Attacks, Added to CISA KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added two critical security flaws impacting WSO2 and Adobe Commerce...
 ANWENDUNGSSICHERHEIT
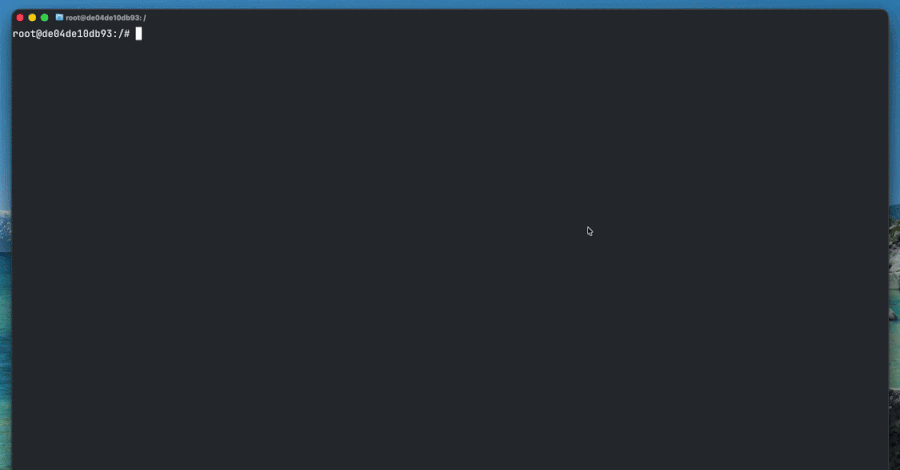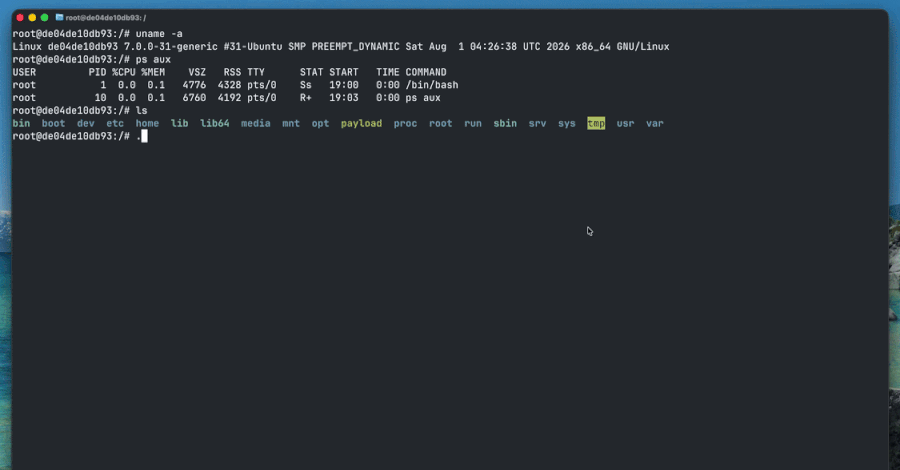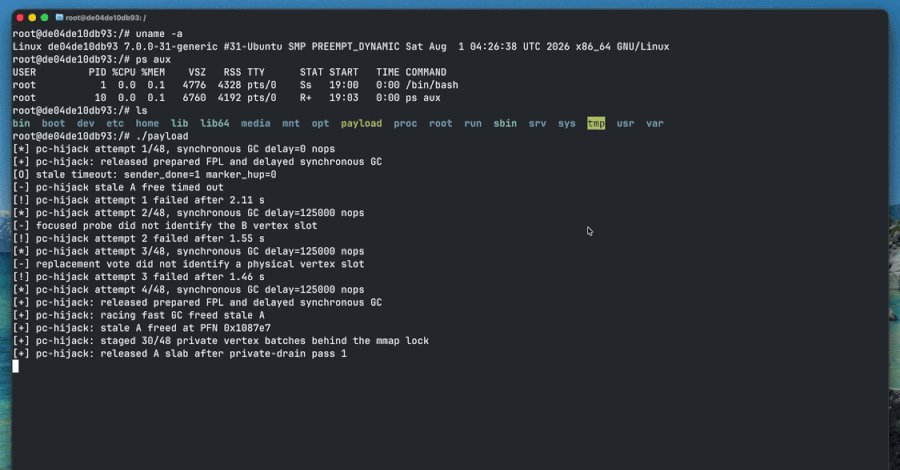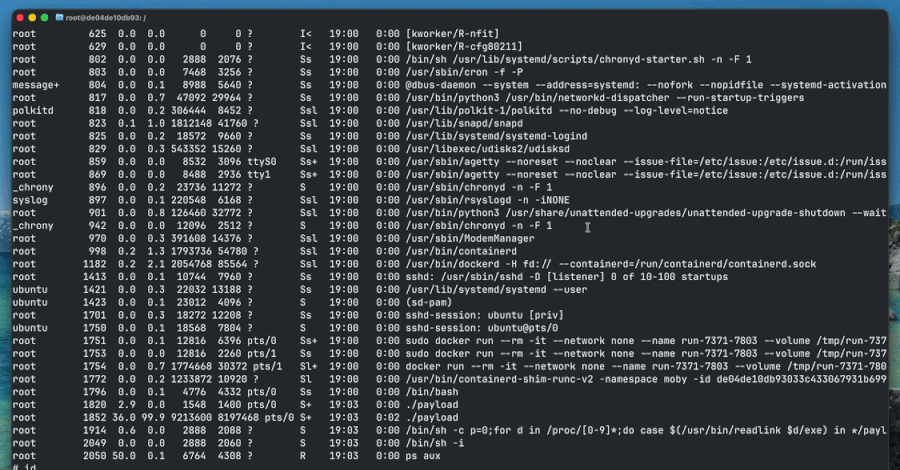
Exploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container Escape
A use-after-free in the Linux kernel's AF_UNIX socket subsystem can be used to escape a container and gain root on...
 ANWENDUNGSSICHERHEIT
A Leaked GitLab Issue Email Address Lets Anyone Push Code and Run CI Jobs as You
The private email address GitLab gives you for filing issues by email is a credential. Anyone who gets it can...