Endpunktsicherheit
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-105307: High Schwachstelle
A vulnerability was detected in Casdoor up to 3.161.1. Affected is the function ApiFilter of the file routers/authz_filter.go of the...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-105290: High Schwachstelle
A vulnerability was determined in feelec-yishu feelcrm-os 1.0.0. This affects an unknown part of the file App/Feelcrm/Index/Controller/GoogleController.class.php of the component...
 ENDPUNKTSICHERHEIT
Russia’s Star Blizzard Targets 100+ Organizations With Fake Event Invites to Deliver Backdoor
Russian state hackers known as Star Blizzard have been using fake event invitations to trick people into installing a backdoor...
 ENDPUNKTSICHERHEIT
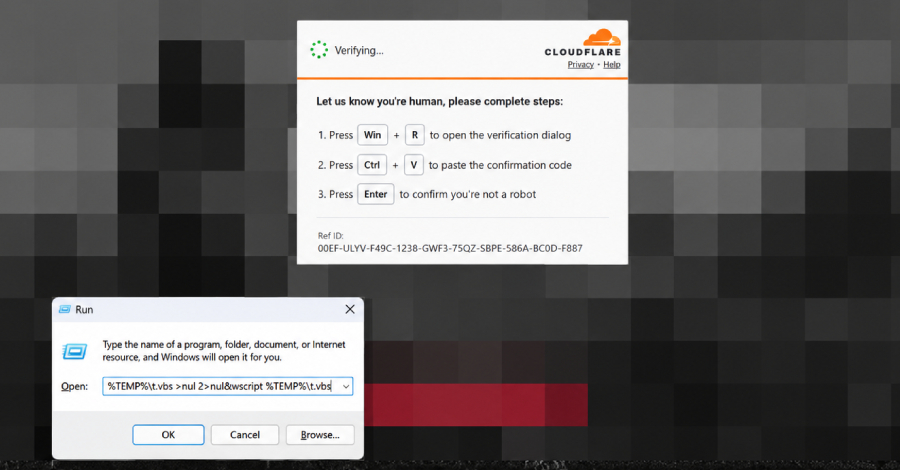
ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits
A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-105148: High Schwachstelle
A vulnerability was identified in SciPhi-AI R2R up to 3.6.6. This vulnerability affects unknown code of the file py/shared/abstractions/llm.py of...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-93549: High Schwachstelle
The CoCart WordPress plugin before 4.9.7 does not scope its REST API authentication filter to its own endpoints, which disables...
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-105215: Critical Schwachstelle
ZITADEL before 3.4.14 and 4.x before 4.16.2 contains an authentication bypass in the hosted Login V1 UI because the 'external...
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-105207: Critical Schwachstelle
ZITADEL 3.0.0 through 3.4.15 and 4.0.0 before 4.17.3 creates links between user accounts and external identity providers without verifying a...
ENDPUNKTSICHERHEIT
The EDR blind spot: 3 ways browser attacks evade endpoint telemetry
Browser-based attacks can steal sessions, abuse extensions, or manipulate users without creating the endpoint artifacts EDR is designed to detect....
 ENDPUNKTSICHERHEIT
Russia’s Star Blizzard Targets 100+ Organizations With Fake Event Invites to Deliver Backdoor
Russian state hackers known as Star Blizzard have been using fake event invitations to trick people into installing a backdoor...