Endpunktsicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-97341: High Schwachstelle
The Visitor Traffic Real Time Statistics plugin for WordPress is vulnerable to Stored DOM-Based Cross-Site Scripting via 'X-Real-IP' HTTP Header...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-87091: High Schwachstelle
The Welcart e-Commerce plugin for WordPress is vulnerable to Stored Cross-Site Scripting via Settlement Notification Parameters in all versions up...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-96267: High Schwachstelle
The WP Visitor Statistics (Real Time Traffic) plugin for WordPress is vulnerable to generic SQL Injection via the 'fullRef' parameter...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-97337: High Schwachstelle
The Simple Membership plugin for WordPress is vulnerable to unauthorized modification of data and sensitive information disclosure in versions up...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-91078: High Schwachstelle
The TillKit WordPress plugin before 1.0.5 does not require the hard-coded, publicly known PIN of the privileged POS account it...
 ENDPUNKTSICHERHEIT
Warlock ransomware breach SharePoint in water, telecom operator attacks
The China-linked ransomware group Warlock targeted a water utility, a telecom provider, a regional government body, and a university by...
 ENDPUNKTSICHERHEIT
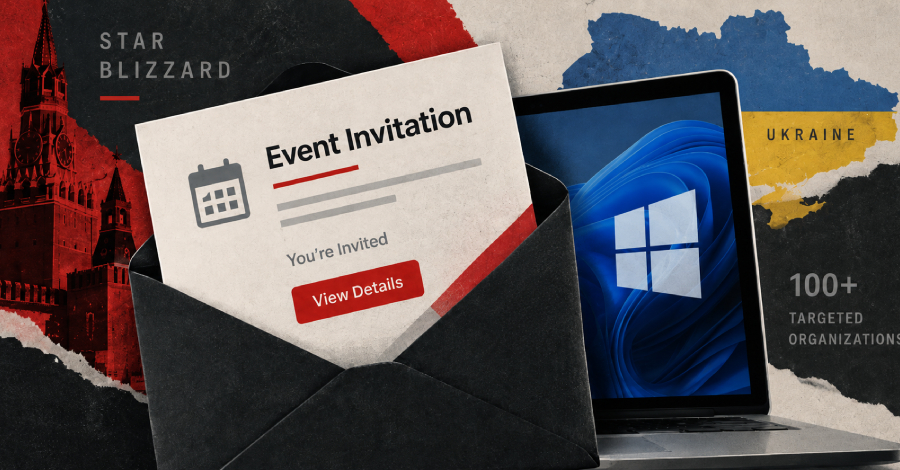
Russia’s Star Blizzard Targets 100+ Organizations With Fake Event Invites to Deliver Backdoor
Russian state hackers known as Star Blizzard have been using fake event invitations to trick people into installing a backdoor...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-12951: Medium Schwachstelle
The Dc Woocommerce Multi Vendor plugin for WordPress is vulnerable to SQL Injection via the 'order_by' parameter of the /multivendorx/v1/compliance/report-abuse...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-97663: High Schwachstelle
The Customer Reviews for WooCommerce plugin for WordPress is vulnerable to Stored Cross-Site Scripting via Comment Author Name in all...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-97342: High Schwachstelle
The JetFormBuilder — Dynamic Blocks Form Builder plugin for WordPress is vulnerable to Stored Cross-Site Scripting via 'choice' Post Meta...