Endpunktsicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-92916: High Schwachstelle
Grav is a flat-file CMS. In Grav 1.7.0 through 1.7.53.2 and 2.0.0 through 2.0.21, when the debugger is enabled (system.debugger.enabled:...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-92919: High Schwachstelle
admin3 through 3.0.0 fails to sanitize client-supplied filenames in the upload handler, allowing authenticated users to write files outside the...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-92918: High Schwachstelle
admin3 through 3.0.0 persists user session tokens in the audit log event body when publishing UserLoggedIn domain events. Attackers with...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-86801: High Schwachstelle
The To Do List Member WordPress plugin from 1.4 through 1.6 ships a file upload endpoint that does not load...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-85130: High Schwachstelle
The WPLP Cookie Consent WordPress plugin before 4.4.4 does not escape a value submitted through a public endpoint for the...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-90823: Critical Schwachstelle
FatPipe MPVPN, WARP, and IPVPN appliances running the end-of-life firmware version 10.1.2r60p100 contain a stack-based buffer overflow in /usr/sbin/auth_user_pass. An...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-90822: Critical Schwachstelle
FatPipe MPVPN, WARP, and IPVPN appliances running the end-of-life firmware version 10.1.2r60p100 contain an OS command injection vulnerability in the...
 ENDPUNKTSICHERHEIT
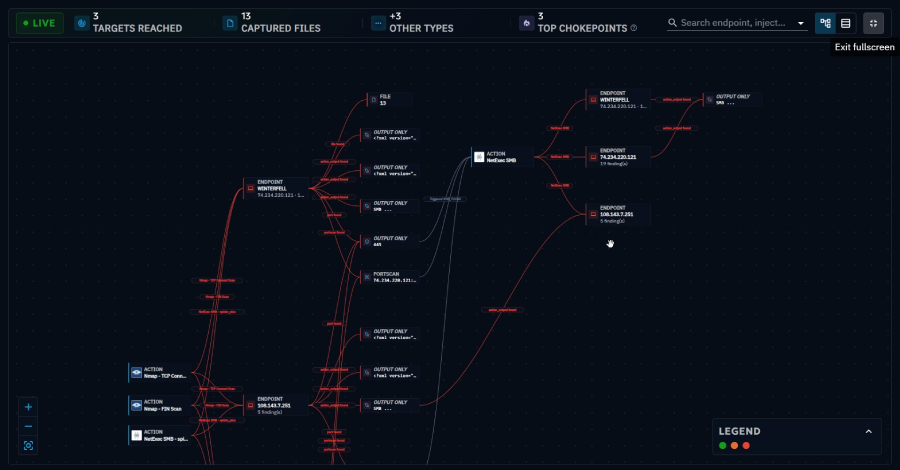
Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point
Introduction Security teams have gotten pretty good at testing against what can hurt them. Can this EDR agent catch this...
 ENDPUNKTSICHERHEIT
RatHat Android Malware Abuses ADB to Retain Shell Access After Uninstall
Cybersecurity researchers have flagged a new Android malware called RatHat that's assessed to be operated by China-based threat actors and...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-27564: High Schwachstelle
A high-privileged remote attacker can exploit a command injection vulnerability in the /api/datastorage/data endpoint by sending a PUT request with...