Endpunktsicherheit
 ENDPUNKTSICHERHEIT
🟡 CVE-2026-37171: Medium Schwachstelle
A lack of tenant separation in SuperTokens Inc. SuperTokens Core v6.0.0 to v11.4.0 allows an authenticated party in one tenant...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-16039: Medium Schwachstelle
The MStore API WordPress plugin before 4.21.0 does not restrict its vendor-orders endpoint to the caller's own orders, allowing any...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-9169: High Schwachstelle
DLL Search Order Hijacking in LUCID Vision Labs Arena SDK 1.0.80.49 on Windows allows a local attacker to execute arbitrary...
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-16038: Critical Schwachstelle
The MStore API WordPress plugin before 4.21.0 does not verify the payment with the payment gateway before marking an order...
 ENDPUNKTSICHERHEIT
Malware Can Abuse Windows Hello for Business Keys for Persistent Entra ID Access
Entra ID researcher Dirk-jan Mollema demonstrated that malware already running in a signed-in Windows session can silently use the victim's...
 ENDPUNKTSICHERHEIT
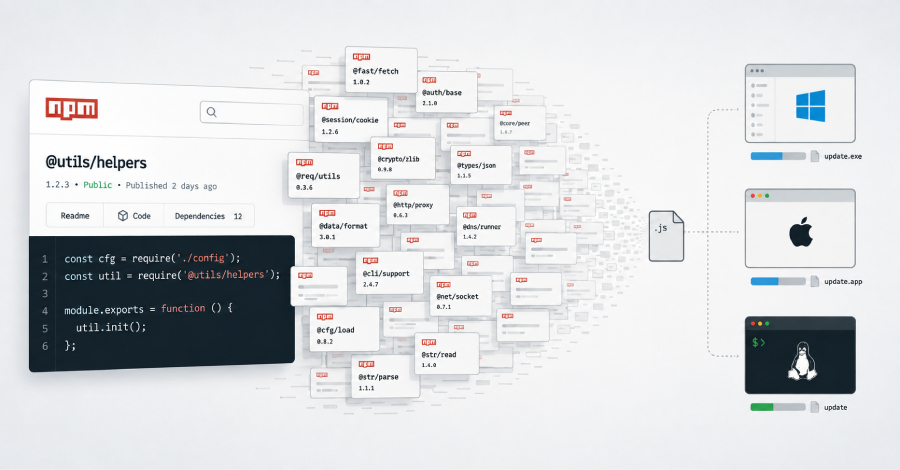
Nearly 800 Malicious npm Packages Deliver Cross-Platform RAT and Infostealer
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-19010: High Schwachstelle
A security vulnerability has been detected in TinyAGI 0.0.20. Impacted is the function processMessage of the file packages/main/src/index.ts of the...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-19009: High Schwachstelle
A weakness has been identified in TinyAGI 0.0.20. This issue affects the function collectFiles of the file packages/core/src/response.ts of the...
ENDPUNKTSICHERHEIT
🔴 CVE-2026-61466: Critical Luecke in Apache Cxf
In Apache CXF's OAuth2 Dynamic Client Registration endpoint, the authorization server accepts and stores the `scope` value supplied in the...
 ENDPUNKTSICHERHEIT
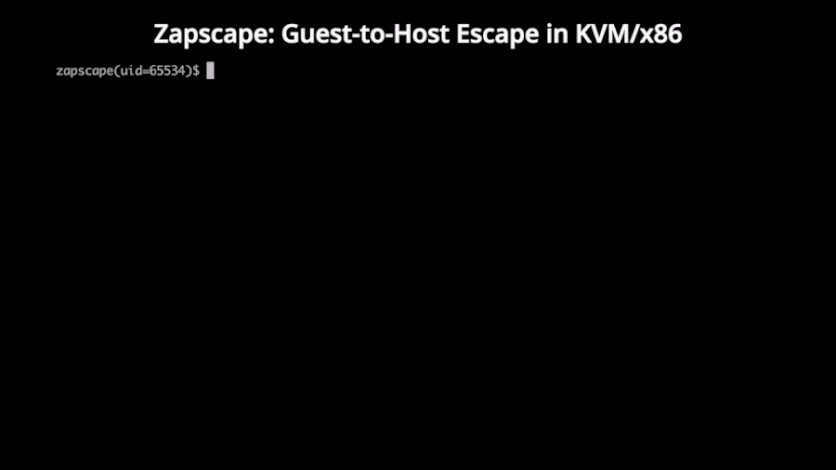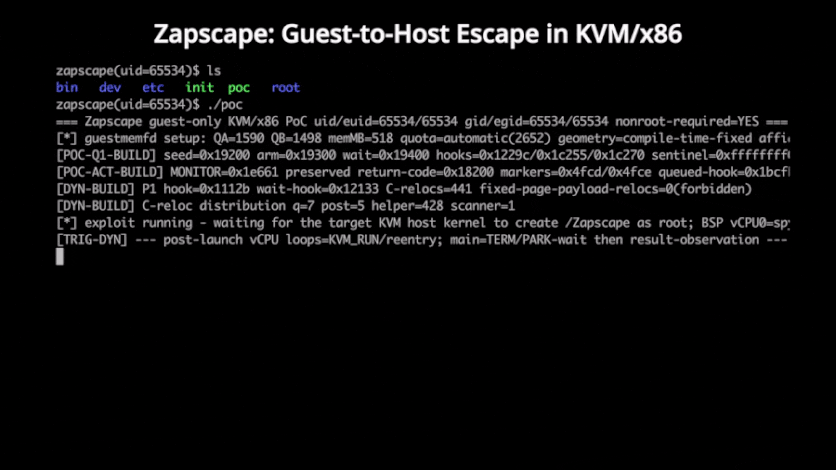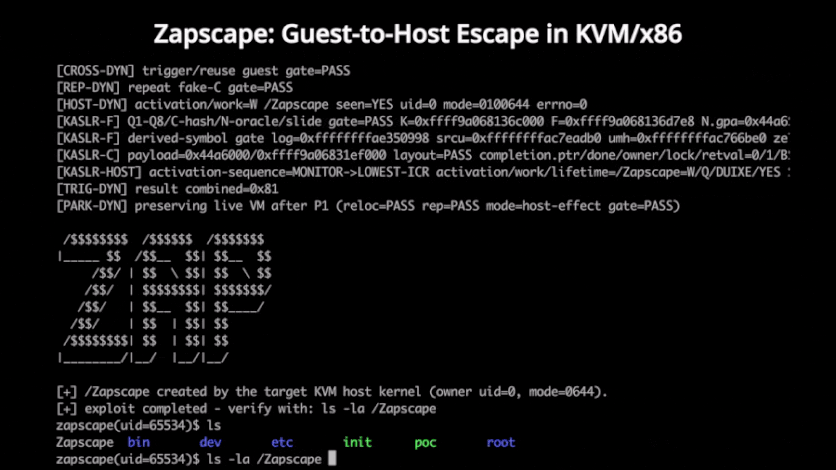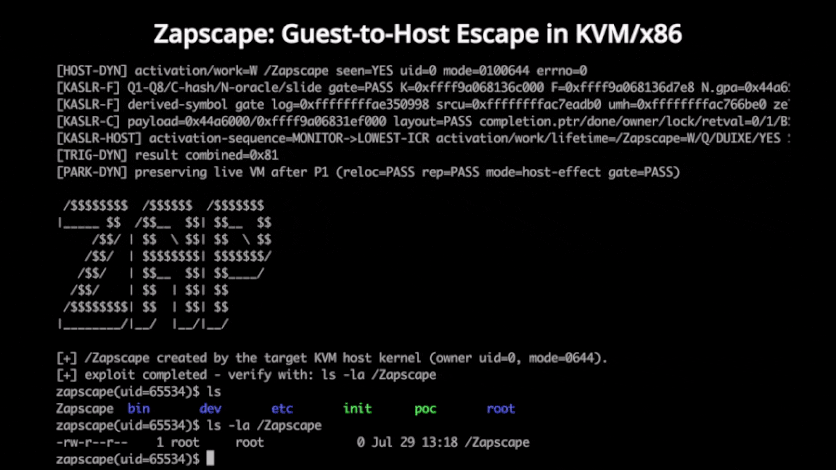
New Zapscape KVM Flaw Could Let Privileged L1 Guest Code Escape to Linux Hosts
Zapscape, a new Linux kernel vulnerability, could allow an attacker with kernel privileges inside an L1 guest virtual machine (VM)...