Endpunktsicherheit
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-45695: Critical Schwachstelle
Kopia is a cross-platform backup tool for Windows, macOS, and Linux with fast incremental backups, client-side end-to-end encryption, compression, and...
 ENDPUNKTSICHERHEIT
New TELEPUZ Malware Spreads via ClickFix to Steal Data and Run Commands
Cybersecurity researchers have called attention to a new modular malware called TELEPUZ that's been spreading via websites infected with ClickFix...
 ENDPUNKTSICHERHEIT
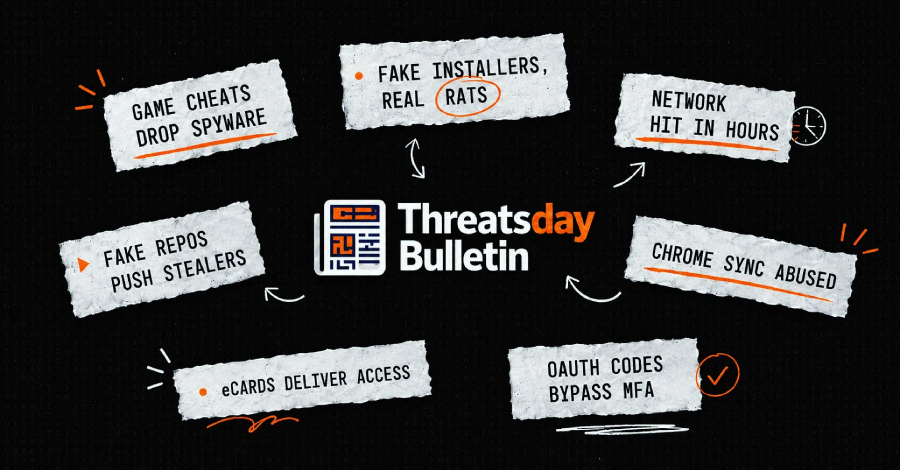
ThreatsDay: Game Cheat Spyware, 24-Hour Ransomware, Chrome Sync Stalking + 12 More Stories
A lot of this week’s trouble starts with something that looks close enough. A familiar repo. A useful installer. A...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-56398: High Luecke in Openwebui Open_Webui
Open WebUI before 0.9.5 contains a stored cross-site scripting vulnerability in the OAuth authentication flow where the picture claim URL...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-61835: High Schwachstelle
Directus is a real-time API and App dashboard for managing SQL database content. Prior to 12.0.0, the SSRF protection on...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-61644: High Schwachstelle
FastGPT is a knowledge-based AI application platform. From 4.14.17 until 4.15.0-beta5, the POST /api/core/chat/record/getCollectionQuote endpoint authenticates the caller's chat and...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-61435: High Schwachstelle
PraisonAI before 4.6.78 contains an authentication bypass in the Call API agent invocation endpoints (src/praisonai/praisonai/api/agent_invoke.py) when PRAISONAI_CALL_AUTH=disabled is configured. The...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-56400: High Luecke in Openwebui Open_Webui
open-webui before 0.3.14 contains a cross-origin resource sharing misconfiguration allowing arbitrary origins with allow_origins=* and authenticated requests to the /api/v1/functions...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-61436: High Schwachstelle
PraisonAI before 4.6.78 fails to verify Svix webhook signatures in AgentMail webhook mode, allowing unauthenticated attackers to forge message.received events....
 CLOUD-SICHERHEIT
🟠 CVE-2026-15583: High Schwachstelle
A confused-deputy flaw in Grafana MCP Server allows an unauthenticated remote attacker to exfiltrate the server's environment-configured Grafana service-account token...