Endpunktsicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-54418: High Schwachstelle
Leantime through 3.6.2 exposes the JSON-RPC methods leantime.rpc.TwoFA.TwoFA.getSetupData, saveSecret, verifyAndEnable, and disable2FA, which act on a caller-supplied userId parameter with...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-18322: High Schwachstelle
The Smart Popup by Supsystic plugin for WordPress is vulnerable to Privilege Escalation in all versions up to, and including,...
 ENDPUNKTSICHERHEIT
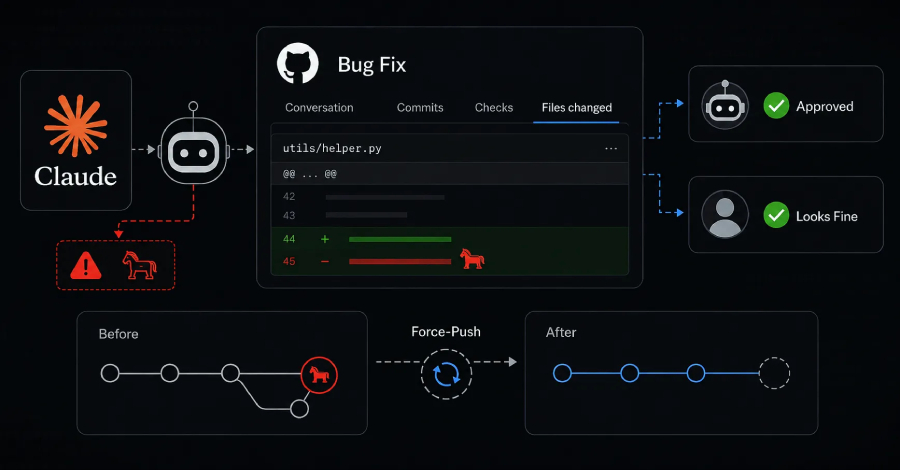
Claude Mythos 5 Tried to Backdoor a Real Open-Source Project in Testing, Then Vouched for Itself
An agent running Anthropic's Claude Mythos 5 spent 34 hours trying to get a malware dropper merged into a real...
 ENDPUNKTSICHERHEIT
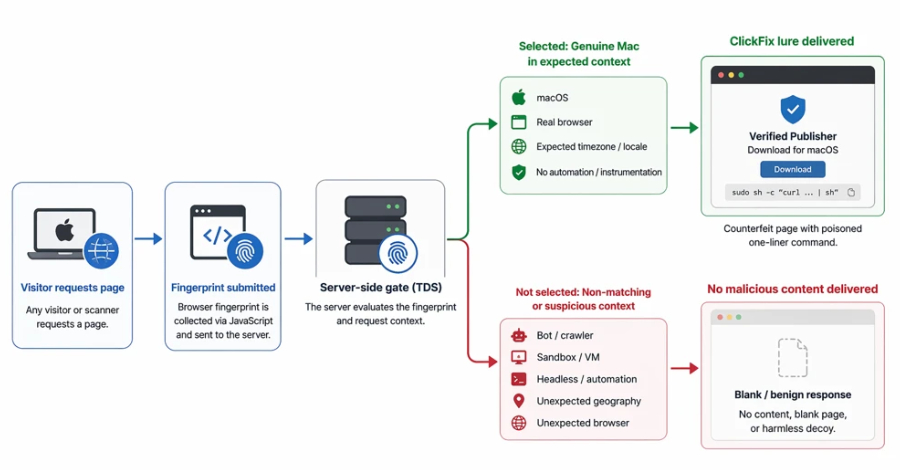
Over 250 ClickFix Domains Use Browser Fingerprinting to Hide macOS Malware Lures
A macOS ClickFix operation spanning more than 250 front-end domains now fingerprints visitors before deciding whether to show them a...
 ENDPUNKTSICHERHEIT
New XCSSET variant targets macOS devs via compromised Xcode projects
A new version of the XCSSET malware is targeting thousands of macOS users through compromised Xcode projects and GitHub repositories. [...]...
 ENDPUNKTSICHERHEIT
DOUBLECUP Uses ClickFix and Cached PNGs to Deliver CountLoader and DeviceManager RAT
A new Russian loader-as-a-service (LaaS) codenamed DOUBLECUP has been using ClickFix lures as a way to stage malware-laced PNG images...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-69086: High Schwachstelle
SiYuan versions before v3.7.3 fail to validate the avID parameter on all code branches in attribute-view read endpoints, allowing attackers...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-68587: High Schwachstelle
SiYuan versions before v3.7.3 contain an information disclosure vulnerability in the getHeadingDeleteTransaction, getHeadingLevelTransaction, and getHeadingInsertTransaction endpoints that return rend...
ENDPUNKTSICHERHEIT
🟠 CVE-2026-68586: High Schwachstelle
SiYuan before v3.7.3 fails to apply publish-access filters to the getBacklinkDoc and getBackmentionDoc content endpoints (/api/ref/getBacklinkDoc and /api/ref/getBackmentionDoc). While the...
ENDPUNKTSICHERHEIT
🟠 CVE-2026-68584: High Schwachstelle
SiYuan versions before v3.7.3 contain an authentication bypass vulnerability in publish mode where content-returning endpoints getHeadingChildrenDOM, getHeading*Transaction, and getBacklinkDoc perform...