Netzwerksicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-90769: High Schwachstelle
Open Notebook before 1.11.0 fails to validate the URL parameter in POST /api/sources endpoint, allowing authenticated users to perform server-side...
 NETZWERKSICHERHEIT
‚TerminalFix‘ Campaign Weaponizes PowerShell for Enterprise Attacks
The ClickFix-style campaign features a sophisticated, multistage attack chain that includes reverse tunnels into victim organizations' networks....
 NETZWERKSICHERHEIT
AI Governance Can’t Wait
Adversaries can manipulate AI defensive reasoning to silently compromise target networks....
 NETZWERKSICHERHEIT
🟠 CVE-2026-77752: High Schwachstelle
The Temporary Login Without Password WordPress plugin before 1.9.9 does not verify that the user requesting a temporary login holds...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-90647: High Schwachstelle
ASE/Kalkitech ASE2000 V2 Communication Test Set 2.35 through 2.37 on Windows contains an improper certificate validation vulnerability in the IEC...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-90651: High Schwachstelle
Socket Firewall (socketdev/socket-registry-firewall) in registry mode before 2.0.0 does not verify upstream TLS certificates by default. When the api_ssl_verify and...
 NETZWERKSICHERHEIT
Dutch NCSC: Critical Check Point VPN flaws exploitation is imminent
The Dutch Nationaal Cyber Security Centrum (NCSC) is warning of imminent exploitation of two critical flaws in Check Point VPN...
 NETZWERKSICHERHEIT
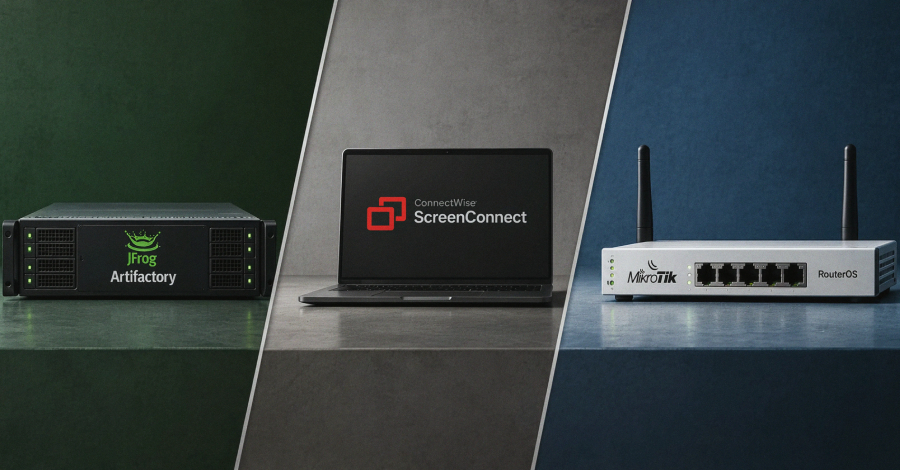
CISA Adds 5 Actively Exploited Artifactory, ScreenConnect, and RouterOS Flaws to KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five security flaws impacting JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik...
NETZWERKSICHERHEIT
🟠 CVE-2026-89178: High Schwachstelle
WeenyGenius, a computer lab management system by Howyar Technologies, has an Origin Validation Error vulnerability. Unauthenticated attackers on the same...
 NETZWERKSICHERHEIT
🟠 CVE-2026-89177: High Schwachstelle
WeenyGenius, a computer lab management system by Howyar Technologies, has a Use of Insecure Protocol vulnerability. Due to the reliance...