Netzwerksicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-61427: High Schwachstelle
PraisonAI before 4.6.78 exposes the MCP HTTP-stream transport without authentication by default: the CLI --api-key option defaults to None, and...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-61435: High Schwachstelle
PraisonAI before 4.6.78 contains an authentication bypass in the Call API agent invocation endpoints (src/praisonai/praisonai/api/agent_invoke.py) when PRAISONAI_CALL_AUTH=disabled is configured. The...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-61430: High Schwachstelle
PraisonAI before 1.6.78 contains a server-side request forgery vulnerability in the web_crawl tool that validates hostnames at check time but...
 NETZWERKSICHERHEIT
Compromised AsyncAPI npm Packages Deliver Multi-Stage Botnet Malware
Four compromised npm packages in the @asyncapi namespace have been observed distributing a multi-stage botnet loader, according to findings from...
 NETZWERKSICHERHEIT
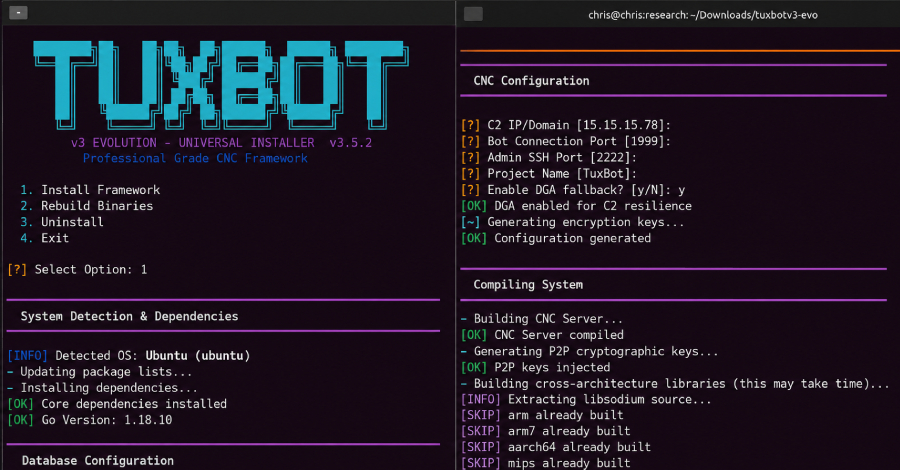
TuxBot v3 Evolution Shows Signs of LLM-Assisted IoT Botnet Development
Cybersecurity researchers have disclosed details of a previously unreported Internet-of-Things (IoT) botnet framework dubbed TuxBot v3 Evolution that shows signs...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-54429: High Schwachstelle
A vulnerability has been identified in SIMATIC S7-PLCSIM Advanced (All versions). Affected devices do not properly handle high-volume multicast network...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12707: High Schwachstelle
Summary Cloudflare quiche was discovered to be vulnerable to memory resource exhaustion due to unbounded queuing of post-handshake client migration...
 NETZWERKSICHERHEIT
🟠 CVE-2024-7708: High Luecke in Eclipse Jetty
For requests that have a body, but reading the body may end up in reading 0 bytes, there is a...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-15416: High Schwachstelle
A flaw was identified in Argo CD, the GitOps engine used by Red Hat OpenShift GitOps, that could allow an...
NETZWERKSICHERHEIT
🔴 CVE-2026-58319: Critical Luecke in Apache Doris
Certain Apache Doris FE HTTP REST administrative APIs were accessible without proper authentication. An unauthenticated attacker with network access to...