Netzwerksicherheit
 NETZWERKSICHERHEIT
HollowByte DDoS flaw bloats OpenSSL server memory with 11-byte payload
A vulnerability dubbed HollowByte allows unauthenticated attackers to trigger a denial-of-service (DoS) condition on OpenSSL servers with a malicious payload...
 NETZWERKSICHERHEIT
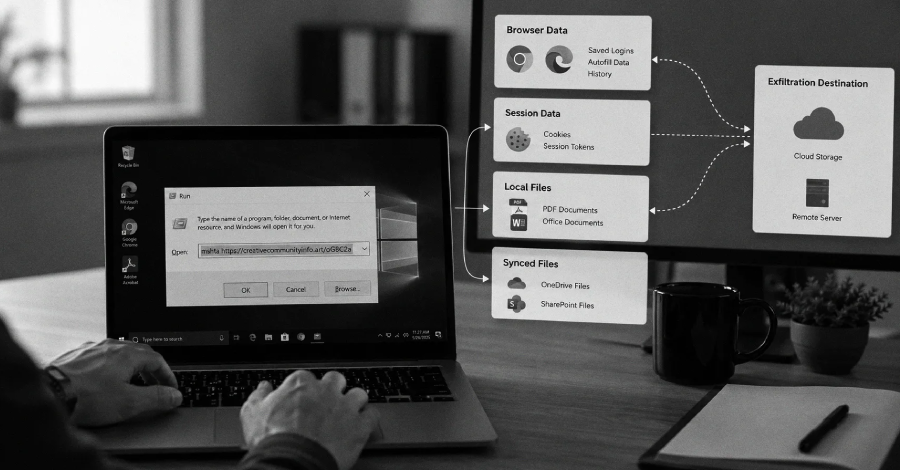
ACR Stealer Uses ClickFix Lures to Steal Browser Tokens and Microsoft 365 Files
ACR Stealer, an infostealer in circulation since 2024, is walking out of enterprise networks with saved browser passwords, live session...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-63306: High Schwachstelle
stoatchat before 0.13.5 contains an unauthenticated server-side request forgery vulnerability in the /proxy and /embed endpoints that accept arbitrary URLs...
 NETZWERKSICHERHEIT
🔴 CVE-2026-14890: Critical Schwachstelle
SGLang uses an expert-parallel backup subsystem that exposes a ZeroMQ PULL socket on a routable network interface that does not...
 NETZWERKSICHERHEIT
Google Gemini CLI abused as a hacking agent, malware botnet operator
A Russian-speaking threat actor known as "bandcampro" used Google's open-source Gemini CLI AI tool as a hacking agent and to...
 NETZWERKSICHERHEIT
New Spirals ransomware encrypts victim network in under 24 hours
A new ransomware actor called Spirals completed a corporate intrusion, from initial access to data theft and encryption, in less...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-61427: High Schwachstelle
PraisonAI before 4.6.78 exposes the MCP HTTP-stream transport without authentication by default: the CLI --api-key option defaults to None, and...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-61435: High Schwachstelle
PraisonAI before 4.6.78 contains an authentication bypass in the Call API agent invocation endpoints (src/praisonai/praisonai/api/agent_invoke.py) when PRAISONAI_CALL_AUTH=disabled is configured. The...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-61430: High Schwachstelle
PraisonAI before 1.6.78 contains a server-side request forgery vulnerability in the web_crawl tool that validates hostnames at check time but...
 NETZWERKSICHERHEIT
Compromised AsyncAPI npm Packages Deliver Multi-Stage Botnet Malware
Four compromised npm packages in the @asyncapi namespace have been observed distributing a multi-stage botnet loader, according to findings from...