Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-7488: High Schwachstelle
Insertion of sensitive information into sent data vulnerability in IKAS Technology Inc. E-Commerce allows Retrieve Embedded Sensitive Data. This issue...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-11575: High Schwachstelle
The PhonePe Payment Solutions WordPress plugin before 3.1.0 does not properly verify the authenticity of incoming payment callbacks: the secret...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2025-60357: High Schwachstelle
AhnLab EPP Management v1.0.14.32-6249 was discovered to contain a NoSQL injection vulnerability via the eventlog/agentEvent/list endpoint.
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-13410: High Schwachstelle
Dancer::Plugin::Auth::Google versions through 0.07 for Perl have TLS verification disabled. The default user agent is initialised with SSL_verify_mode explicitly disabled....
 ANWENDUNGSSICHERHEIT
🔴 CVE-2024-23564: Critical Schwachstelle
HCL Aftermarket EPC is affected by Business Logic Vulnerability using which a non valid user of the application can obtain...
 ANWENDUNGSSICHERHEIT
The Race to Field Military Autonomy Is On, Can Trusted Information Infrastructure Keep Pace?
Military forces are under increasing pressure to field autonomous capabilities faster than ever before. Across the U.S., UK, and NATO,...
 ANWENDUNGSSICHERHEIT
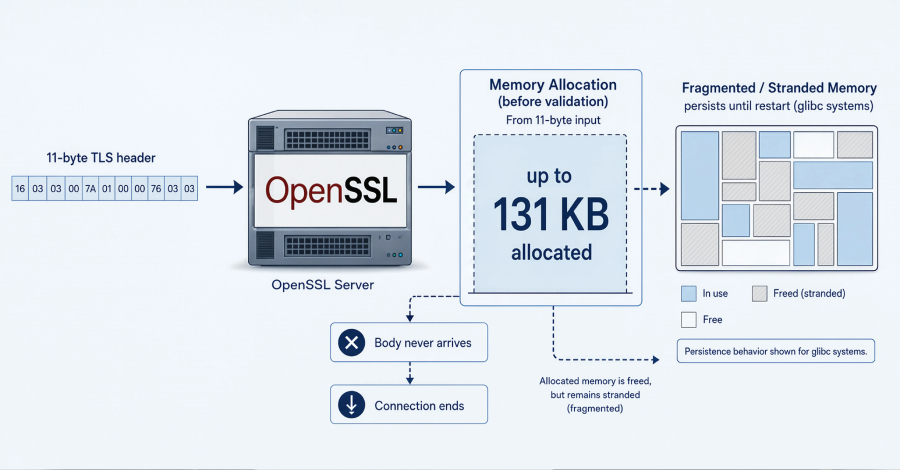
OpenSSL HollowByte Flaw Could Freeze Server Memory with 11-Byte TLS Requests
Eleven bytes will make an unpatched OpenSSL server set aside up to 131 KB of memory for a message that...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-13755: Medium Schwachstelle
The Tickera – Sell Tickets & Manage Events plugin for WordPress is vulnerable to Stored Cross-Site Scripting via 'price_wrapper' Shortcode...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-44596: Medium Luecke in Spaceapplications Yamcs
Yamcs is a mission control framework. Prior to 5.12.7, the authentication endpoint POST /auth/token in yamcs-core, handled by yamcs-core/src/main/java/org/yamcs/http/auth/AuthHandler.java, lacked...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-55440: Medium Schwachstelle
Microsoft UFO open-source framework for intelligent automation across devices and platforms. Prior to 3.0.7, the COMMAND_RESULTS handler in ufo/server/ws/handler.py called...