Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-41870: High Schwachstelle
Missing Authorization, Improper Control of Generation of Code ('Code Injection'), Improper Control of Dynamically-Managed Code Resources, Use of Externally-Controlled Input...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-80099: High Schwachstelle
Several Newfold plugins are vulnerable to Authentication Bypass. The vulnerability exists because the plugins bundle the wp-module-data module. In the...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-14359: High Schwachstelle
The YITH WooCommerce Waitlist Premium plugin for WordPress is vulnerable to Privilege Escalation in versions up to, and including, 3.35.0....
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-41869: Critical Luecke in Apache Nutch
Missing Authorization, Improper Resource Shutdown and Job Interruption vulnerability in Apache Nutch Server (Nutch REST API). This issue affects Apache...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-16272: Critical Schwachstelle
Use of less trusted source vulnerability in PayTR Payment and Electronic Money Institution Inc. PayTR Virtual Pos iFrame API (v9x)...
 ANWENDUNGSSICHERHEIT
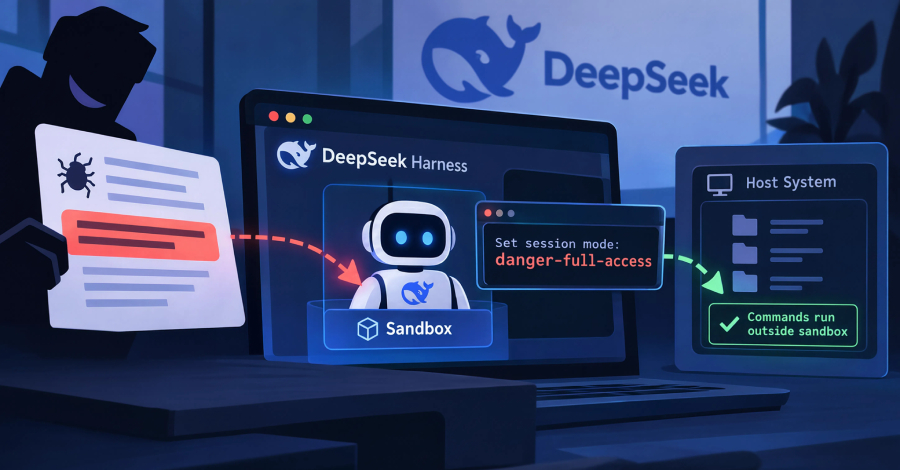
DeepSeek Harness Flaw Let AI Agents Disable Their Own File Sandbox Without Approval
A flaw in DeepSeek Harness, DeepSeek's open-source tool for running AI coding agents on a developer's machine, let a sandboxed...
 ANWENDUNGSSICHERHEIT
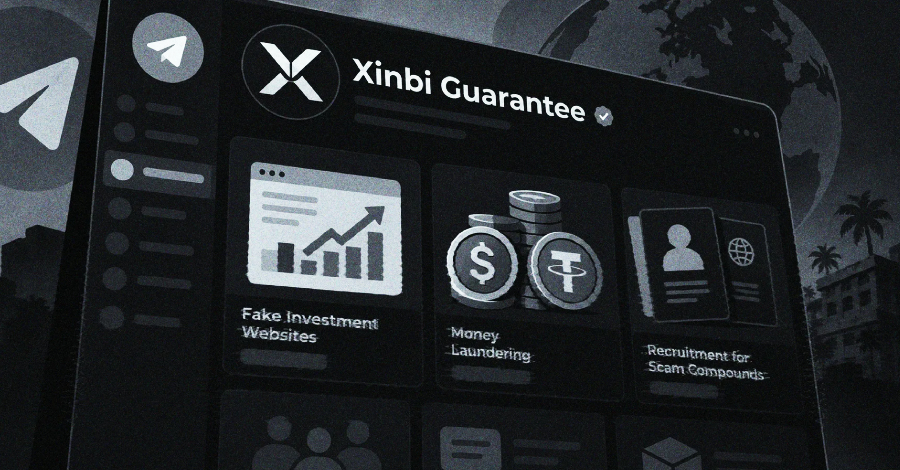
U.S. Disrupts Xinbi Guarantee Scam Marketplace, Freezes $52.8 Million in Crypto
The U.S. Department of Justice (DoJ) on Wednesday announced coordinated actions aimed at an illicit online marketplace called Xinbi Guarantee...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-62646: High Schwachstelle
A vulnerability has been identified in Reyrolle 7SR5 (All versions < V2.70). A session identifier is generated using an algorithm...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-73316: High Schwachstelle
XenForo before 2.3.13 contains a payment replay vulnerability in the PayPal REST payment provider that allows attackers to process the...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-73314: High Schwachstelle
XenForo before 2.3.13 contains a signature verification logic error in the PayPal REST webhook handler that allows unauthenticated attackers to...