Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100636: High Schwachstelle
SiYuan versions before v3.8.4 contain a path traversal vulnerability in the exportBrowserHTML endpoint that allows authenticated administrators to write arbitrary...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100643: High Schwachstelle
SiYuan versions before v3.8.4 fail to properly escape four stored Attribute View values in textarea elements, allowing authenticated attackers to...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100646: High Schwachstelle
SiYuan is a self-hosted personal knowledge management system. In versions up to and including 3.8.3, the kernel's authentication guards (CheckAuth...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100627: High Schwachstelle
Capgo (Cap-go/capgo.app) server backend Supabase functions contain an incorrect authorization flaw in the API-key bundle promotion path. The PUT /bundle...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100676: High Schwachstelle
January, the media proxy/embed service of stoatchat (stoatchat/stoatchat), before version 0.15.5 improperly resolves SVG values as local filesystem paths when...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100608: High Schwachstelle
Flowise through 3.1.4 does not enforce authorization on the BullMQ admin dashboard. When the server runs in queue mode with...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100639: High Schwachstelle
SiYuan v3.8.3 fails to HTML-escape the data-subtype attribute when generating gutter-button markup (app/src/protyle/gutter/button.ts, assigned via innerHTML in app/src/protyle/gutter/index.ts) from co...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100623: High Schwachstelle
Capgo (capgo.app) exposes the legacy membership table public.org_users directly through Supabase PostgREST. The table's row-level security policies "Allow org admin...
ANWENDUNGSSICHERHEIT
🔴 CVE-2026-18143: Critical Schwachstelle
The Request a Quote for WooCommerce plugin for WordPress is vulnerable to Arbitrary File Upload in all versions up to,...
 ANWENDUNGSSICHERHEIT
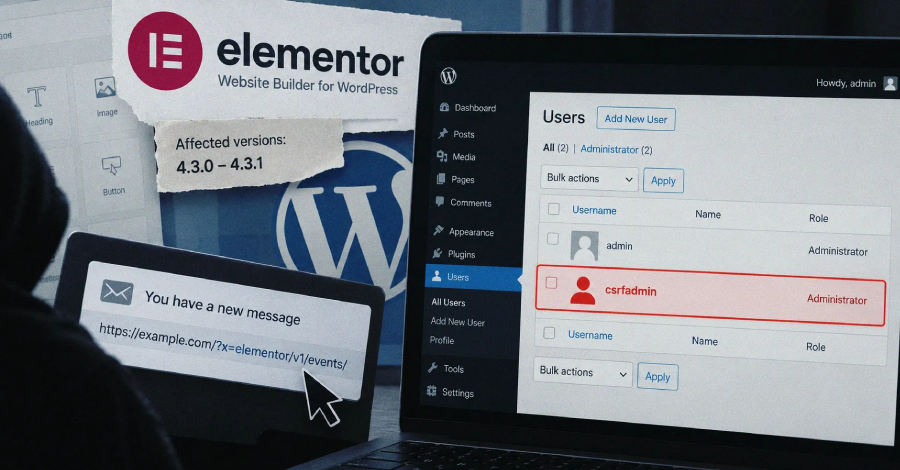
Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link
Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by...