Endpunktsicherheit
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-63800: Critical Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: pNFS: Fix use-after-free in pnfs_update_layout() When hitting the NFS_LAYOUT_RETURN branch...
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-53399: Critical Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: nfsd: release layout stid on setlease failure nfs4_alloc_stid() publishes the...
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-53398: Critical Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: NFSD: Fix SECINFO_NO_NAME decode error cleanup nfsd4_decode_secinfo_no_name() currently initializes sin_exp...
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-53384: Critical Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: serial: 8250_dw: unregister 8250 port if clk_notifier_register() fails dw8250_probe() registers...
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-63795: Critical Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: 9p: avoid putting oldfid in p9_client_walk() error path When p9_client_walk()...
 ENDPUNKTSICHERHEIT
20+ Hijacked Government Websites Became an Attack Channel
More than 20 Brazilian government websites were hijacked and turned into malware delivery channels in an active PhantomEnigma campaign uncovered...
 ENDPUNKTSICHERHEIT
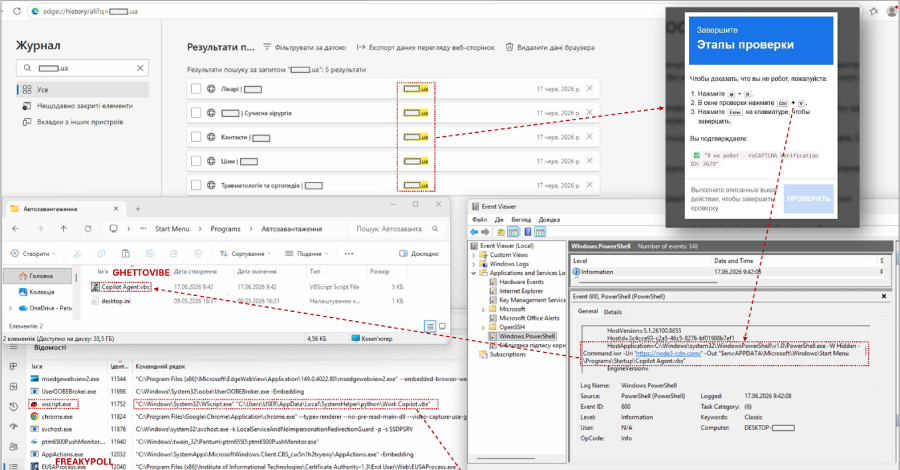
UAC-0145 Uses ClickFix CAPTCHAs to Infect Ukrainian Devices wih Malware
Russian state-sponsored threat actors have been observed leveraging the infamous ClickFix strategy to trick Ukrainian targets into infecting their own...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-16210: High Schwachstelle
A vulnerability was found in newpanjing simpleui 2026.01.13. This affects the function self.get_action of the file simpleui/admin.py of the component...
ENDPUNKTSICHERHEIT
🟠 CVE-2026-16209: High Schwachstelle
A vulnerability has been found in Gerapy up to 0.9.13. The impacted element is an unknown function of the file...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-9323: High Schwachstelle
The urwid web display backend (urwid/display/web.py) generates web session identifiers (urwid_id) in Screen.start() by concatenating two random.randrange(10**9) calls that use...